Centraleyes Resource Center
- Centraleyes was featured by NJBIZ as one of 13 enterprise-ready startups graduating from the NJ FAST fintech and AI accelerator.
- Centraleyes named a Sample Vendor in the Gartner® Hype Cycle™ for Cyber-Risk Management, 2026
- How Neurosoft and Centraleyes Transform Compliance from Cost to Strategy
- Compliance Without Chaos: Automating Multi-Framework, Multi-Entity & Multi-Region Compliance
- Frost & Sullivan Names Centraleyes a Leading Innovator in 2026 Compliance Automation Radar.
- Centraleyes Recognized in Frost Radar™: Compliance Automation, 2025
- Yair Solow Featured on Bugy's Founder Interviews
- Centraleyes Chosen as Global Top 5 Startups of the Year - Interview
- Centraleyes on Cyber Ghost: Interview with Yair Solow
- Spotlight Q&A with Centraleyes at Safety Detectives
- Centraleyes Expands Automated Risk Register To Cover All Enterprise Risk
- New Centraleyes 4th Generation Release Officially Goes Live
- Yair Solow Featured on VPN Mentor
- Yair Solow on CNN
- CyGov Signs a Strategic Agreement with R3 (Spanish)
- Centraleyes Welcomes Co-Founder of Optiv, Dan Burns, to Its Board of Directors
- Centraleyes Continues to Expand Its Global Network of Strategic Partners with UK-based ITC Secure
- Centraleyes Introduces First Automated Risk Register
- Yair Solow Featured on Website Planet
- Trevor Failor named head of sales at CyGov
- CyGov is rebranding its platform as Centraleyes
- Cybersecurity Company Cygov Partners With Risk Management Company Foresight
- CyGov agrees strategic partnership with top 200 MSSP Cybriant
- Cyber Resilience Resource for Businesses Re-Deploying Remotely
- The Four New Pillars of Corporate Protection Yair Solow on InfoSecurity Magazine
- CyGov selected by SixThirty as Top Cyber Security Startup
- Europe's Top Cyber Security Startups
- CyGov Interviewed by MediaSet
- Eli Ben Meir's article in Security Intelligence
- Yair Solow on i24 News
- CyGov Selected by WorldBank
- Eli Ben Meir OpEd in the Houston Chronicle
- Yair Solow and Eli Ben Meir Present at the SparkLabs Demoday 8
- Apollo Data Breach Shows the Risk Behind a Simple Phone Call
- NIST Draft Puts IoT Cybersecurity Into the Risk Management Process
- China-Linked Hackers Targeted Medical and Military Research Through REDCap in Long-Running Attack
- EDPB Moves Toward a Common GDPR Breach Notification Template
- The TanStack Breach and the Fragility of Trusted Code
- The IBM Italy Breach Puts Third-Party Infrastructure Risk Back in Focus
- Copy Fail Explained
- Google Says North Korea Was Behind the Axios npm Supply Chain Attack
- Colorado Moves to Revise Its Landmark AI Law After Industry Pushback
- Lloyds Banking Group Investigates Mobile App Data Exposure Affecting Multiple UK Banks
- How Chinese Hackers Reached America’s Surveillance Infrastructure
- Figure Breach Enters New Phase After Data Leak Claims
- California Fines Disney $2.75 Million in Record CCPA Case
- Security Researchers Breach Moltbook in Record Time
- SoundCloud Data Breach: 29.8 Million Accounts Exposed
- Betterment Confirms Security Incident After Unauthorized Crypto Message
- Massive Instagram Data Scare Ties 17.5M Accounts to Leak, But Meta Denies Breach
- Android Security Update Triggers Renewed Attention with Mid-Month Changes
- Marquis Data Breach Exposes Hundreds of Thousands of Bank Customers
- Chinese Hackers Exploited a Zero-Day in Cisco Email Security Systems
- U.S. Threatens Penalties Against European Tech Firms Amid Regulatory Fight
- SoundCloud Confirms Security Incident
- Prosper Marketplace Data Breach Expands: 17.6 Million Users Impacted in Database Intrusion
- Inside the UK’s AI Sandbox: Where Innovation Plays by New Rules
- Inside the F5 Breach
- Qantas Data Breach Exposes Millions, Tied to Wider Salesforce Campaign
- Italy’s AI Law Comes Into Force
- Harrods Data Breach Explained
- Volvo Breach: A Closer Look at the Technical and Organizational Gaps
- Chinese Hackers Breach U.S. Firms as Trade Tensions Rise
- SonicWall Confirms Unauthorized Access to MySonicWall Backup Files
- Jaguar Land Rover Confirms Data Breach After Cyberattack Disrupts Global Operations
- Behind the Salesforce OAuth Drift Breach
- Hackers Threaten Google Following Data Exposure
- TransUnion Data Breach Exposes 4.5 Million Records Through Third-Party App
- FBI Issues Updated Warning on Salt Typhoon’s Global Cyber-Espionage Operations
- Apache ActiveMQ Breach Reveals Unusual Attacker Behavior
- Ransomware Disrupts Inotiv Operations
- Workday Confirms Data Breach Tied to Salesforce Attacks
- Nvidia and AMD Agree to Revenue Share with the US as Security Scrutiny Intensifies
- Global Shared Controls
- Enhance Your Cyber Maturity With ITSM Integration and Automated Remediation
- Ensure Your Ongoing Compliance With Automatic Framework Reassessment Tasks
- Stay in the Know With a Full Activity Log of Your Assessment Collection
- Add a New Entity to Perform Your Assessment in 10 Seconds
- Quantify Financial Risk With Centraleyes Platform Primary Loss Calculator
- Cover Your Entire Environment With Centraleyes's Risk Application Assessments
- Communicate Cyber Risk With Your Executives in an Intuitive, Beautifully Visualized Board Reporting
- Stay on Top of Your Vendors' Cyber History With In-Depth External Scans
- Automate the Creation and Maintenance of a Risk Register, Saving Hours on Manual Work
- Add a New Framework and Distribute Assessments in Your Organization
- View Your Organization's Risk Scoring Through the NIST Tiering Lens
- Framework Navigation Tool: An Intuitive Way to Manage Compliance
- Always Prepared for the Next Task With Automated Remediation
- Effective Team Work With Drag-and-Drop Control Assignment
- Get Real-Time Critical Alerts That are Specifically Relevant to You
- MSSPs Can Manage Multiple Clients Under One Platform
- Onboard a New Vendor in Just 30 Seconds
- Centraleyes Vendor Risk Profile: Turn Hours of Work Into Seconds
- Always Informed with Centraleyes Domain Benchmarking
- How to Build a Successful GRC Program to Help Reduce Your Risk Posture
- How to Stay Secure and Compliant in a World of Regulatory turmoil
- Don’t Keep Your Head in the Clouds – How to Protect Yourself from Virtual Risk
- Flash Webinar: When It's Time to Build a Risk Management Program
- Enhancing Cyber Risk Management Through Automation: Webinar
- Flash Webinar: From Technical to Business Risk - How to Communicate With Your Board
- Flash Webinar: What You Can Learn From the SolarWinds Attack to Lower Your Chances of Being Breached
- Flash Webinar: Supply Chain and Third-Party Vendor Risk
- Flash Webinar: Cyber Risk Management Doesn't Have to Be Painful
- 8 Best AI Powered GRC Tools in 2026
- 6 Best Operational Risk Management Software Platforms in 2026
- NIST 800-171 Revision 3: The Impact on CMMC Compliance
- What Are the Key Components of HIPAA? 2026 Breakdown
- Best Cybersecurity Risk Assessment Software for GRC Teams in 2026
- NIST Cybersecurity Framework 2.0: Guide for All Sectors
- 9 Best Supplier Risk Management Tools in 2026
- Best 11 SOC 2 Compliance Software for Fast-Growing Companies in 2026
- Top 11 ISO 27001 Compliance Tools to Get Certified Faster
- 7 Top Vendor Onboarding Software Platforms for Third-Party Risk Teams
- Best 12 Compliance Audit Software Platforms for SOC Readiness
- 6 Top Risk Register Software Tools for Security Teams in 2026
- Best Policy Management Tools in 2026
- Essential Eight Maturity Levels Explained: How to Plan Cybersecurity Uplift
- 11 Best ERM Software in 2026: The Complete Guide
- The Complete List of the Best Internal Audit Management Software
- 8 Enterprise GRC Software Solutions Worth Knowing in 2026
- Australian Information Security Manual: Key Updates and How to Stay Compliant
- 10 Best Cyber Risk Management Platforms of 2026
- Top NIST Compliance Software Platforms for Cybersecurity Teams in 2026
- Top 6 Compliance Management Tools for Financial Services in 2026
- How Compliance Outsourcing Helps Streamline Security and Strengthen Oversight
- Top 8 Cynomi vCISO Platform Alternatives for 2026
- AI Governance Tools: 9 Best for 2026, Compared
- Best 8 ESG Reporting Tools for 2026
- How Much Does Essential Eight Compliance Cost in 2026?
- Best 12 Compliance Risk Assessment Tools for 2026
- Best 12 Third-party Risk Management Software in 2026
- GRC Software Pricing: What It Actually Costs in 2026
- Top 9 AI Compliance Tools of 2026, Compared
- What Software Should I Choose for ESG Management?
- The 12 Best GRC Tools for 2026
- The Attacks Email Security Policies Help Protect Against
- PCI DSS Fines: Potential Costs and Financial Impact
- Building an Effective Access Control Policy: A Step-by-Step Guide
- Top 10 Industry-Recognized GRC Certifications for Risk and Compliance Professionals
- CCPA vs CPRA: What You Need To Know About California’s Data Privacy Framework
- How To Create an Effective Vendor Management Program
- Which Businesses Are Required to Submit a PCI ROC?
- The 15 Best GRC Conferences to Attend in 2026
- Cyber Leaders of the World: Chris Lockery, CISO at Help at Home
- Cyber Leaders of the World: Michael Anderson, CISO at the Dallas Independent School District
- Cyber Leaders of the World: Timothy Spear, Co-Founder and CTO of Whonome
- Cyber Leaders of the World: Marc Johnson, CISO at Impact Advisors
- Cyber Leaders of the World: Craig Williams, CISO at Secure Data Technologies
- Cyber Leaders of the World: Bill Genovese, CIO Advisory Partner at Kyndryl
- Cyber Leaders of the World: Dr. Brian Callahan, Graduate Program Director & Lecturer at ITWS@RPI, and CISO at PECE
- Cyber Leaders of the World: Chris Grundemann, Research Category Lead for Security and Risk at GigaOm
- Cyber Leaders of the World: Barak Blima, CISO at CHEQ
- Cyber Leaders of the World: Tony Velleca, CEO at CyberProof and CISO at UST
- Cyber Leaders of the World: Rob Black, CEO and Founder of Fractional CISO
- Cyber Leaders of the World: Zachary Lewis, CISO at the University of Health Sciences and Pharmacy in St. Louis
- Cyber Leaders of the World: Dan Wilkins, CISO at the State of Arizona
- Cyber Leaders of the World: Sagar Narasimha, CISO at Amagi
- Cyber Leaders of the World: Seema Sharma, Global Head of Information Security & Data Privacy at Servify
- Cyber Leaders of the World: Shay Siksik, VP of Customer Experience at XM Cyber
- Cyber Leaders of the World: Raz Karmi, CISO at SimilarWeb
- ISO 27001 Operations Security
- RCSA (Risk and Control Self-Assessment): Purpose & Process
- Risk Management Process
- ISO 27001 Data Retention Policy
- Data Silos
- Risk Compliance Certification
- Risk Documentation
- Compliance Posture
- Double Materiality Assessment
- GRC Requirement
- IT Risk Management (ITRM)
- PCI Compliant Hosting
- Audit Risk Model
- Surveillance Visit
- Recovery Point Objective
- FIPS (Federal Information Processing Standards)
- HIPAA Covered Entities
- ISO 9001 Audit
- GRC Convergence
- DoD Distribution Statements A–F: Meanings & Rules
- Continuous Monitoring: When It's Used & How It Works
- CMMC Accreditation Body (Cyber AB): Role & Process
- FedRAMP Baselines: Impact Levels, Controls & Monitoring
- SOX Controls: Key Sections, Control Types & Effectiveness
- CUI Enclave: Uses, Components & Role in CMMC
- Processing Integrity: How It Works in SOC 2 & Examples
- Document Control Procedure: Purpose & Key Components
- ISO 27001 Data Destruction: Clauses & Controls
- HIPAA Enforcement Rule: How Enforcement & Penalties Work
- vCISO: Services, Qualifications & Cost Models
- PCI Non-Compliance Fees: Who Issues Them & When They Apply
- NIST Incident Response Life Cycle: The Four Phases
- HIPAA Omnibus Rule: What It Changed & Who It Affects
- Business Continuity Plan (BCP): Components & Template
- Human Resource Security Policy: Purpose & Common Components
- Fraud Risk Assessment: Process & Key Components
- Supplier Performance Risk System (SPRS): How to Calculate Scores
- Audit Exception: Meaning, Examples & vs. Audit Finding
- Managed Security Service Provider (MSSP): Role & How to Choose
- PA-DSS: Requirements & Transition to PCI Secure Software
- What Should Be Included in a Security Policy?
- What is the first step of PCI DSS compliance?
- What's the Difference Between TX-RAMP, StateRAMP, and FedRAMP?
- ISO Standards for AI: ISO/IEC 42001 and Related Standards
- What’s the difference between NIST 800-53 and NIST 800-171?
- Which AI Compliance frameworks can I choose?
- What is the difference between cloud governance and cloud compliance?
- What are the types of compliance risk?
- What are the benefits of continuous risk management?
- What is the difference between risk assessment and risk analysis?
- What are the Benefits of cyber risk quantification?
- How to Achieve Continuous Compliance?
- How do you implement continuous controls monitoring?
- What is a maturity assessment process?
- What are the different types of compliance management tools?
- What are the Differences Between Internal and External Penetration Testing?
- What is the difference between proactive and reactive risk management?
- Why is a data retention policy important?
- What is the operational risk management process?
- How to implement the COSO framework?
- How do you perform a cyber security risk assessment?
- How to develop an enterprise risk management framework?
- How do you respond to a security questionnaire?
- What are the main steps in the threat modeling process?
- What exactly is considered PHI according to HIPAA?
- What does the PCI Compliance Auditor Look At?
- How to Detect and Prevent Data Leakage?
- What are the Challenges Associated with Cloud Security Management?
- How Many Tactics and Techniques Are in MITRE ATT&CK?
- What Are the Benefits of Conducting a Risk Assessment?
- What are the categories of controls in ISO 27001?
- How Does ABAC Differ From Other Access Control Models?
- What Does a Compliance Management System Look Like?
- What Are the NIST CSF Implementation Tiers?
- What is the Purpose of Compliance Attestation?
- How do I become NIST 800-171 compliant?
- Why are the three rules of HIPAA necessary?
- What are the seven categories of risk?
- What are the Six Types of Vulnerability Scanning?
- Which are the most important compliance frameworks?
Resources | News & Updates
Emergency Update for Apple Devices
Apple has released emergency security updates to address two zero-day vulnerabilities that have already been exploited in…
Operation Cookie Monster
On Tuesday, more than a dozen law enforcement organizations from around the world shut down the Genesis…
Centraleyes Launches the First of its Kind Higher-Ed Cyber Risk Program in Collaboration with FSU
The key objective is to bring hands-on training and experience on best practices and the key role…
Call for Restraint in the Race to AI
Is the World Adopting AI Models Too Fast? That’s what an elite group of tech leaders and…
Saks Fifth Avenue Added to GoAnywhere Victim List
Dozens of organizations have been added to Clop ransomware’s victim list over the last couple of months,…
Beware: SVB’s Collapse Being Exploited By Scammers
Cybersecurity experts caution that scammers are profiting from the turmoil caused by the collapse of Silicon Valley…
New TSA Regulations for Airlines Facing “Persistent Cybersecurity Threats”
The Transportation Security Administration on Tuesday announced regulations to force airports, along with aircraft owners and operators,…
CISA Calls on Tech Developers to Put Security into Digital Products
CISA called on technology development companies to “fundamentally shift” product design to one that puts cybersecurity at…
Social Engineering “Smishing” Attack on Coinbase
Coinbase and other crypto platforms are frequently targeted by fraudsters. That’s because currency in any form is…
GoAnywhere Impact Setting In
An attack on the GoAnywhere controlled file transfer software that exploited a recently discovered zero-day vulnerability has…
GoodRx Gets a Taste of its Own Medicine
GoodRx has recently come under fire for breaking its privacy promises and the HBNR (Health Breach Notification…
Malicious Apps Abused Microsofts Verification Standard
In December, a group of threat actors abused the Microsoft “certified publishers” status of the Microsoft Cloud…
Drop in Ransomware Payments Show Victims Becoming Bold
A report conducted by Chainalysis noted a 40% drop in payments made to ransomware extortion groups in…
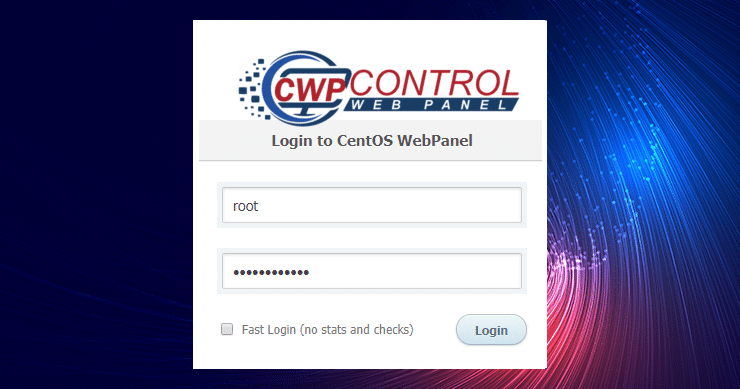
POC of CWP Flaw Leads to Live Attacks
The popular and free Control Web Panel software has a significant security flaw that has already been…
What Can’t You Do With Chat GPT?
Since its release, there has been an explosion of interest in Chat GPT in the media and…
Centraleyes Launches NIST 7621 Risk Framework for Small Business
Centraleyes announces the addition of NIST 7621 to its extensive framework library. The NIST 7621 framework provides…
Google Sued Again For Deceptive Location Tracking
Google settled two privacy lawsuits last week. The data and information goliath will pay $9.5 million to…
LastPass Attacker Did Reach Password Vaults
What does your human logic dictate? Using third-party password managers like LastPass, sometimes thought to be more…
Game Over for Epic
Fortnite developer, Epic Games, was charged a whopping $275,000,000 penalty in settlement fees in violation of federal…
Centraleyes Goes Live with the Latest Version of ISO 27001 2022 Standard
The ISO 27001 standard is internationally accepted as a specification for an Information Security Management System (ISMS).…
96% of Classroom Apps Share Student’s Personal Data
Internet Safety Labs, a non-profit organization on a mission to ensure online product safety, released a new…
Will the FBI Block Tik Tok?
On Friday, Christopher Wray of the FBI raised concerns that Chinese owned Tik Tok “is in the…
Massive Twitter Leak
Chad Loder, the founder of cyber security awareness company Habitu8, received evidence last week of a massive…
World Cup Cyber
This Sunday marked the commencement of the FIFA World Cup in Qatar, and threat actors will be…
FTX Has Been Hacked
On Friday, crypto exchange FTX recommended users delete FTX apps and avoid using its website, backing up…
Insurance Giant Settles Groundbreaking Lawsuit with Oreo Cookie Brand Mondelez
A settlement was reached last week in a $100,000 lawsuit between Zurich, a global insurance giant, and…
White House Convenes Ransomware Summit
A two-day International Counter Ransomware Summit was held this past Monday and Tuesday. Leaders and experts from…
FBI Warns of Iranian Hacking Group Ahead of Elections
Misinformation and disinformation are pressing problems that have mingled with traditional cybersecurity to evolve into a form…
Verizon Verifies Data Breach
Verizon notified an unknown volume of its prepaid customers that attackers breached Verizon accounts and were able…
Nullmixer Malware Madness
Using a single Windows executable file, Nullmixer infects devices with 12 different streams of malware, all at…


