

Centraleyes announces the addition of the New York Department of Financial Services (NYDFS) Cybersecurity Regulation to its extensive framework library. The NYDFS is a set of rules issued by...

Centraleyes announces the addition of PCI DSS to its extensive framework library. The PCI DSS refers to any entity that stores, manages or transmits cardholder data, such as retailers,...

Centraleyes announces the addition of the ISO 22301 Business Continuity Management Framework to its expanding framework library. ISO 22301 is an international standard for Business Continuity Management. It offers...

Centraleyes announces the addition of the new South African data privacy framework, the Protection of Personal Information Act (POPIA), to its expanding framework library. POPIA establishes a minimal baseline...

Centraleyes announces the addition of the Secure Controls Framework (SCF) to its expanding framework library. The Secure Controls Framework is a comprehensive catalog of controls that enables companies to...
Updated November 2026: this list was published in 2022 and covers events held that year; all dates below have passed. Check each organizer's website for current events. Organizations across...

Centraleyes announces the addition of the Cyber Resilience Review (CRR) security assessment to its expanding framework library. CRR is a lightweight, interview-based assessment method that was created by the...

Centraleyes has recently announced the addition of the UAE IA compliance regulation to its expanding framework library. The goal of the UAE IA Regulatory is to assist institutions within...

Centraleyes is excited to announce the addition of ISO 27701 security standard to its expanding framework library. ISO 27701 establishes guidelines and describes standards for implementing, designing, maintaining and...
Data is big business these days. You don’t need to look further than Google’s advertising program to see how lawfully gained user data supports the company’s primary source of...
What is UK Cyber Essentials? Cyber Essentials is a government-backed scheme that was created to help organisations of all sizes protect themselves from a wide range of common cyber...

Centraleyes is happy to announce the addition of OWASP MASVS security standard to its expanding framework library. The Open Web Application Security Project (OWASP) is a non-profit international organization...

Centraleyes is happy to announce the addition of the Insider Risk Mitigation security standard to its expanding framework library. This risk framework is intended to help business owners and...
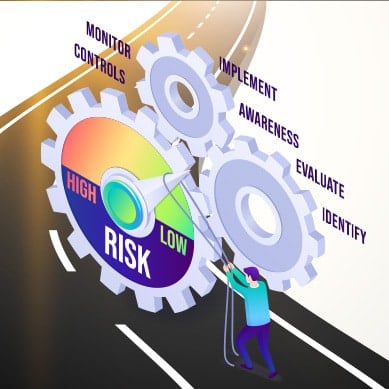
Every aspect of a business is affected by ESG from its very inception through to production and market share. Incorporating ESG compliance at every stage is not only necessary...
As far back as the early 1900s, special laws and government agencies were beginning to pop up across the world to deal with environmental issues. There was a surge...
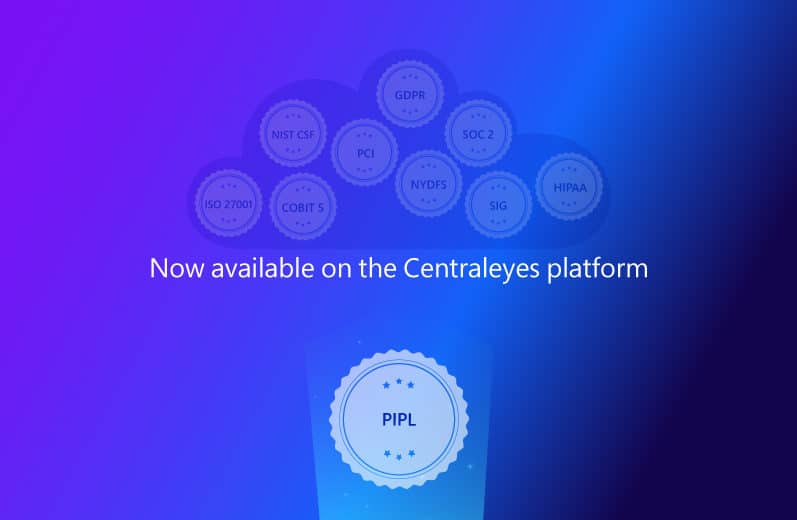
Centraleyes is happy to announce the addition of the Personal Information Privacy Law (PIPL) of China to its expanding framework library. Centraleyes has added the PIPL questionnaire as one...

Centraleyes is excited to announce the upgrade of the new CMMC version 2.0 in its extensive framework library. This new version released by the CMMC replaces version 1.02 and...
Environmental, Social and Governance (ESG) issues are a regular part of mainstream consciousness and are continuously gaining support. ‘Hybrid’, ‘upcycling’ and ‘diversity’ are a part of everyday vernacular and...

Centraleyes is proud to announce the addition of the Nevada Revised Statutes (NRS), Chapter 603A to its extensive control inventory. The addition of NRS to the Centraleyes framework library...

Centraleyes is excited to announce the addition of the Ransomware Readiness Assessment (RRA) Model to its expanding framework library. Centraleyes has added the RRA to its control inventory, allowing...
What is the ESG reporting framework? ESG stands for Environmental, Social and Governance. It’s become a popular measurement for assessing the quantitative and qualitative aspects of an investment’s environmental,...
Modern enterprise networks and infrastructures are complex. Working with several different networks, cloud services, and remote workers means a growing infrastructure that needs to be protected to ensure integrity...
Centraleyes continues to expand its framework library, with the latest addition of the CIS Top 20 Critical Controls. The CIS Critical Security Controls (CSC) are published by the Center...
Note: This blog reflects on CIS Controls Version 7.1, providing historical context and comparing it to Version 8. In a world where data breaches are a daily occurrence, implementing...
If your business or organization operates in the healthcare space, you are most probably familiar with HIPAA (Health Insurance Portability and Accountability Act). It was introduced by Congress in...
The COVID-19 crisis has thrown up innumerable challenges for businesses. With remote working becoming part of everyday reality, it has significantly increased the challenge of cyber security. In order...
The technology sector is constantly evolving and with it, the collection, retention and use of personal data. In the European Union, this is something that GDPR was designed to...
Running a company is never simple. But for companies that do business in the State of California, things just became more complicated. On January 1, 2020, the state’s landmark...