

How To Create an Effective Vendor Management Program
Key Takeaways A strong vendor management program gives you a structured way to choose, review, monitor, and…

CMMC v2.0 vs NIST 800-171: Understanding the Differences
Key Takeaways CMMC 2.0 enforcement began in 2025 via DFARS clause 7021 CMMC is moving from policy…
How the OWASP ASVS Helps Improve Software Security
A short time ago, we announced our integration of OWASP ASVS into our cyber risk management platform.…
Massachusetts Data Privacy Law: MIPSA and S.2619 Status
Updated November 2026: the 2022 MIPSA bill did not become law. A new bill, S.2619, is in…
New York Privacy Act: 2026 Status and Requirements
Status as of November 2026: New York has no comprehensive consumer privacy law. The New York Privacy…
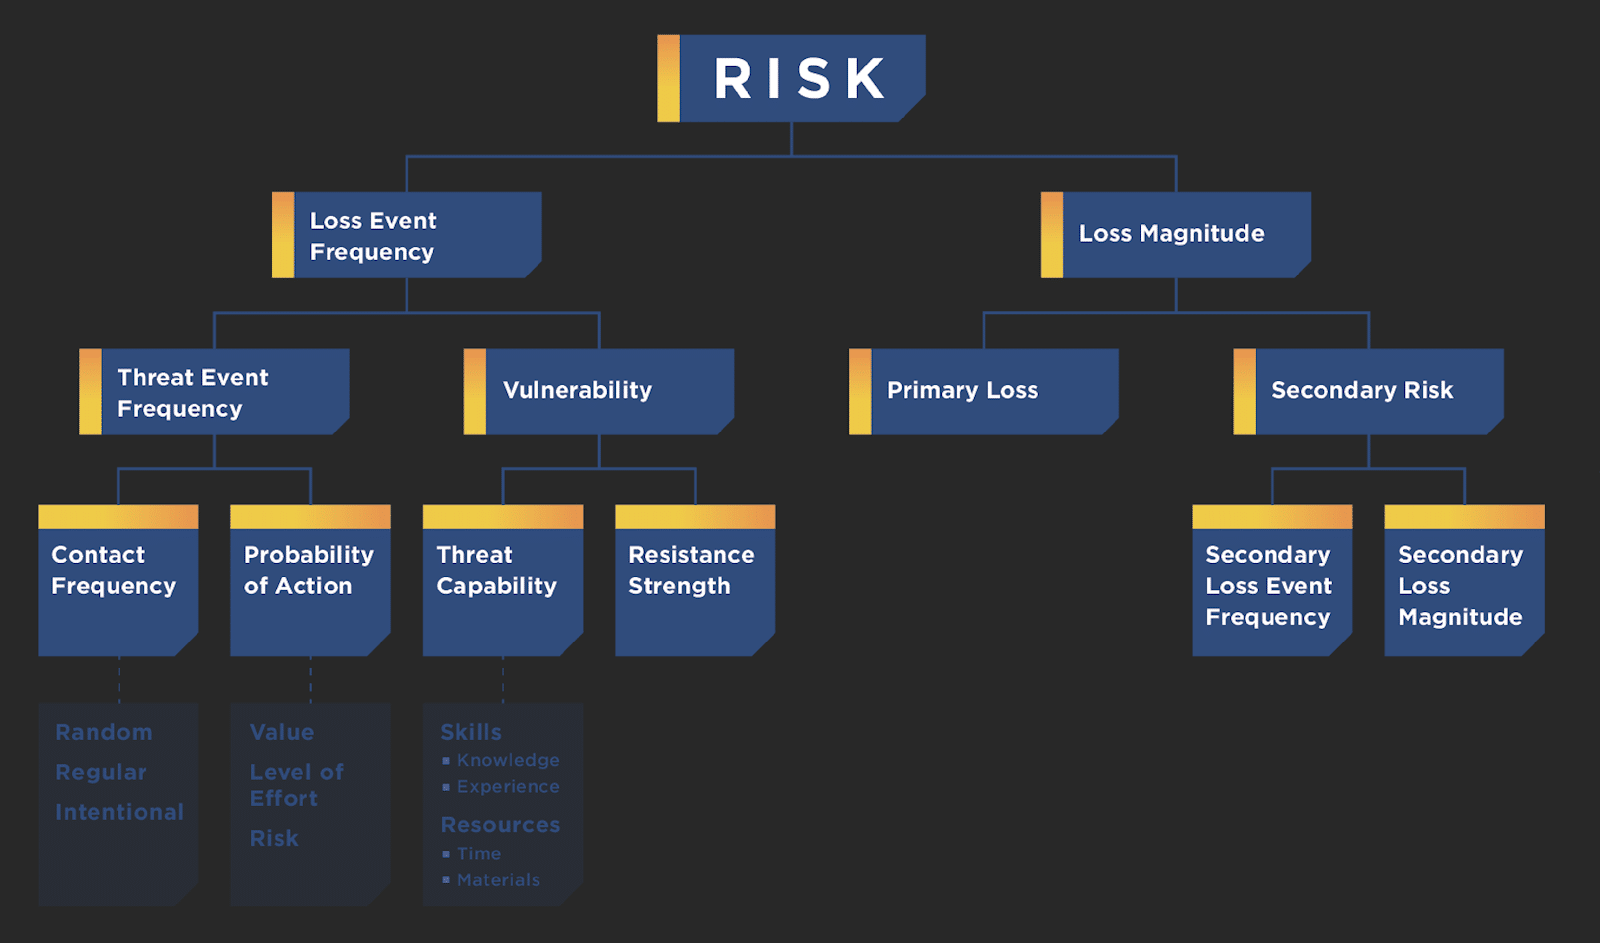
FAIR Model Risk Management - Pros and Cons
Information risk is not just a technical problem but affects the bottom line and daily activities of…
4 Critical Capabilities for Cyber Risk Management Tools
Cybersecurity is top of mind for most businesses today. A single data breach can compromise your ability…
Everything You Need to Know About UK Cyber Essentials
What is UK Cyber Essentials? Cyber Essentials is a government-backed scheme that was created to help organisations…
Why Modern Risk Management Demands a Hybrid Approach
An ounce of prevention is worth a pound of cure. Decision-makers would do well to remember this.…
How to Integrate an ESG Framework into Your Risk Management Plan
Every aspect of a business is affected by ESG from its very inception through to production and…
How Automating Audit Workflows Streamlines the Process
Every audit will involve an official inspection and thorough examination of your company: its IT systems, networks,…
ESG Risk Management: How to Assess, Analyze & Prioritize Risks
As far back as the early 1900s, special laws and government agencies were beginning to pop up…
How IT Risk Management Impacts Your Organization
No business is without risk — and anyone who believes otherwise is due for a rude awakening. …
Cybersecurity Incident Response Plan: Why Your Business Needs One
Imagine if you knew someone was about to break into your house. With adequate time to prepare,…
Why Board Members Should care about ESG Compliance Software
Environmental, Social and Governance (ESG) issues are a regular part of mainstream consciousness and are continuously gaining…
How to Implement a Vulnerability Management Program
Between the shift to distributed work, the growth of the Internet of Things, and the troubling surge…
How to Choose a GRC Platform for Your Company
Every great company has a sound business plan. It encompasses knowledge and expertise, evaluates the market, calculates…
What Does Compliance Automation Enable for Your Business?
Compliance has long been a thorn in the side of IT departments — not in the least…
How To Develop a Cybersecurity Risk Management Plan
Cybercrime is on the rise in virtually every industry. Today’s businesses are facing an unprecedented threat landscape…
How Insurance Companies Can Leverage Cyber Risk Management
Last year set multiple records for cyber crime, and none of them were good. DDoS attacks soared…
Top 5 Cybersecurity Tips for Your Organization During the Holidays
The holiday season gives malicious actors the perfect opportunity to attack your organization’s systems to obtain sensitive…
M&A Cybersecurity Due Diligence Best Practices
Mergers and acquisitions (M&A) are intended to boost the value of your brand or business when you…
Cyber Risk Management for Private Equity Investment Portfolios
The goal of any investment is to generate a positive return on that investment—so that part’s obvious.…
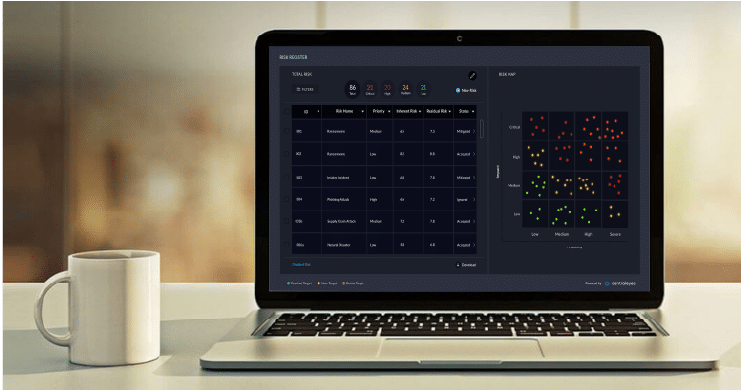
Centraleyes Introduces a Next-Gen Enterprise Risk Register
With our most recent update to Centraleyes, we’ve introduced a next-generation risk register that allows clients full…
What Is a Compliance Management System? A Quick Overview
Whether you work in retail, pharmaceuticals, manufacturing, or another industry, your business must follow government regulations if…
How to Approach Cybersecurity Risk Assessment: 4 Steps
Digitization has made both our personal lives and business workflows more convenient and efficient than ever, but…