
August 2026 update: FedRAMP Rev. 5 remains available during the transition to FedRAMP 20x, the newer cloud-native certification path. The 2026 program uses FedRAMP Certified terminology and certification Classes...
What is a PCI Audit? The Payment Card Industry Data Security Standard, known widely as PCI DSS, is a set of security standards intended to ensure that ALL businesses...
What is DORA (Digital Operational Resilience Act)? DORA is a groundbreaking EU regulation designed to enhance the operational resilience of the financial sector. It aims to tackle the challenges...
The digital era has brought new levels of attention to the privacy debate. From big data breaches in fortune 500 companies to small-scale fraud, it’s clear public perception is...
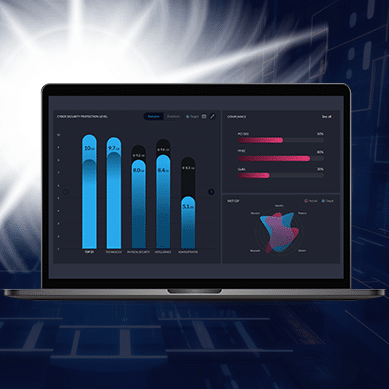
Updated November 2026: PCI DSS v4.0.1, published in June 2024, is now the current version of the standard. PCI DSS v4.0 was retired on December 31, 2024. Centraleyes proudly...
PCI DSS v4.0.1 is the current version of the Payment Card Industry Data Security Standard. Published in June 2024, it clarified PCI DSS v4.0 without adding or removing requirements....
Beyond the clouds, the sky appears vast and unrestricted, seemingly without any constraints. However, the truth is quite different. International rules govern the airspace, ensuring safety and order for...
Updated November 2026: the ADPPA (H.R. 8152) was reported by the House Energy and Commerce Committee in 2022 but never reached a House floor vote and was not enacted...

And Then There Were Ten The Texas Data Privacy and Security Act (HB4) was approved by the Texas Senate on May 10, 2023. Greg Abbott, the governor of Texas,...

Updated November 2026: Montana's applicability thresholds were lowered and the cure period removed by SB 297, effective October 1, 2025. What is the Montana Consumer Data Privacy Act (MTCDPA)?...
What is the SIG Questionnaire? The SIG, short for “Standardized Information Gathering (Questionnaire)”, standardizes the assessment of vendors and other third parties. This recognized repository of questions spans 18...
The key objective is to bring hands-on training and experience on best practices and the key role of technology to the future leaders of Cyber Risk and Compliance Centraleyes...
This is a 2023 news post. For where Iowa’s law stands today, see our Iowa privacy law tracker. Iowa joined the privacy club last week when it passed a...
IRS Publication 4557, Safeguarding Taxpayer Data (current revision: Rev. 6-2024) is the IRS guide that shows tax professionals how to protect client data and comply with the FTC Safeguards...
Updated November 2026: North Dakota still has no comprehensive consumer privacy law. No comprehensive consumer data privacy bill was introduced in the 2023 or 2025 regular sessions. During the...
The California Privacy Rights Act (CPRA) is the amendment to the California Consumer Privacy Act (CCPA) that California voters approved as Proposition 24 in November 2020. Its changes took...
What is ISO 27002:2022? Before we get started, let’s take a minute to explain exactly what ISO 27002 is. ISO/IEC 27002:2022 is an information security standard published by the...
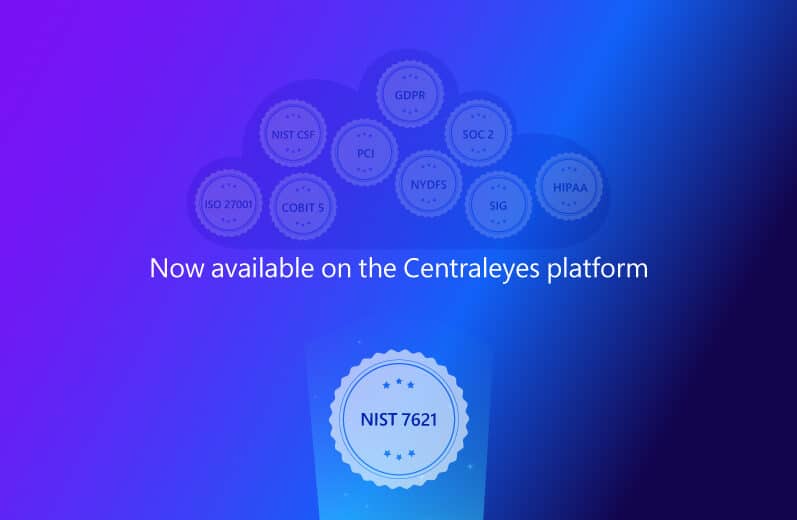
Centraleyes announces the addition of NIST 7621 to its extensive framework library. The NIST 7621 framework provides guidance on how small businesses can provide basic security for their information,...

The ISO 27001 standard is internationally accepted as a specification for an Information Security Management System (ISMS). It is one of the most widely used information security principles worldwide...
Cyber attacks and ransomware threats on small businesses may not reach the headlines, but they pose a serious risk to businesses and their consumers. Small businesses are the core...
Virginia Takes a Lead in Data Privacy Just eight pages long, the VCDPA is significantly more succinct than the California Consumer Privacy Act (CCPA). That’s not to say that...
The Concept of Zero Trust In the past, companies focused security policies on controlling network perimeters, assuming that everything inside the network was safe. But as corporate data footprints...
CIS Controls The Center for Internet Security (CIS), a non-profit organization with a mission to develop and disseminate cyber defense best practices to organizations around the world, has developed...
2026 Update: Where CPA Compliance Stands Now The Colorado Privacy Act has moved into the enforcement phase. Recent legislative changes and regulatory clarifications signal that regulators are focusing more...

Centraleyes announces the addition of NIST 800-53 to its extensive framework library. NIST 800-53 was created to provide federal agencies with standards and guidelines for protecting and managing their...

Centraleyes announces the addition of the Higher Education Community Vendor Assessment Toolkit (HECVAT) its extensive framework library. HECVAT is a risk assessment template that was created specifically for higher...

Centraleyes announces the addition of the Federal Financial Institutions Inspection Council (FFIEC) to its expanding framework library. The FFIEC is a structured interagency body made up of five banking...
The way that your company conducts itself has never been more critical. Approximately 76% of consumers say they will stop buying from companies that do not respect the environment,...
The SEC Proposes New Cybersecurity Standards In March 2022, the SEC (Securities and Exchange Commission) released the Cybersecurity Risk Management, Strategy, Governance, and Incident Disclosure proposal. These guidelines are...
The days of businesses thinking exclusively in terms of revenue are over. Now more than ever, companies need to be aware of their environmental, societal, and governmental impact. After...