

Effective risk management becomes paramount amid the dynamic landscape of global risks and persistent economic uncertainties. At the heart of this risk spectrum lies market risk – the threat...

The regulatory landscape is constantly in flux, shaped by advancements in digital technology, shifting societal expectations, and global interconnectedness. Organizations now face many regulations that impact their operations, data...
Environmental, Social, and Governance (ESG) metrics have emerged as key indicators for organizations seeking to demonstrate their commitment to sustainability and responsible business practices. Through exploring ESG metrics across...
Cyber insurance offers financial protection and support in the event of a cyber attack, data breach, or other cyber-related incidents. Ironically, the security that insurance brings to policyholders stands...
Organizations around the world are grappling with a fresh array of challenges and risks. From record-breaking inflation and economic slumps to the relentless proliferation of cyberattacks and geopolitical instability,...
Forrester recently published a report on the growing trend of CISOs turning to cyber risk quantification models to assist board-level decision-making. But before jumping on the bandwagon, it’s important...
The global pandemic has undeniably caused significant disruptions in people’s lives and businesses. While business leaders understandably have learned to prioritize crisis management, operational resilience, environmental initiatives, and employee...
The California Consumer Privacy Act (CCPA) was introduced to empower individuals with greater control over their personal information and hold businesses accountable for data handling practices. For organizations operating...
Unpatched Vulnerabilities Cause Massive Breaches Vulnerability management can be the difference between safeguarding your organization or setting up your business for a professional disaster. Think T-Mobile, and Twitter, and...
Organizations face an ever-growing array of cyber challenges. The traditional manual approaches to security are no longer sufficient to combat the cultivated tactics employed by the modern malicious actor....

While the Internet offers consumers a veritable wealth of information, goods, and services, it is also a rich source of data regarding consumers. Through “cookies” and other tracking technologies,...
According to BitSight, the financial services industry is a high-value target for threat actors. Firms in this sector are 300 times more likely to be targeted by a cyberattack...
Quantitative risk analysis refers to a numeric projection of the total impact of a given risk on business objectives. A risk quantification model is a tool or approach that...

What is Information Security Automation? Security automation refers to the use of technology and tools to automate recurring functions in the field of information security such as detecting, investigating,...

In a world where cyber risks lurk in the dark shadows of our networks, one thing is crystal clear. You need a cybersecurity risk management strategy in place to...

What is Vulnerability Management? Vulnerability management is a critical element of information security. With cyber-attacks and data breaches increasing in both quantity and complexity, it is of utmost importance...

What is Digital Risk? Digital risk is the term for the negative effects that result from implementing new digital technology. Strong benefits of digital technology, such as improved customer...

Introduction For almost any business, being compliant with regulations is an important part of operating efficiently. However, in some industries, it’s critical to maintain regulatory compliance or else face...

Privacy a Growing Risk for Students Along with this explosion in the growth of online learning tools comes the inherent risks of exploitation and concerns over student privacy. This...

What is EdTech? Short for education technology, EdTech includes applications and digital technology used in primary, secondary, and corporate training to enhance the educational experience in different areas, such...
What Is an Attack Surface? Your “attack surface” is a susceptible area comprised of points in a network, system, or application at which an intruder could try to gain...

Data breaches can have far-reaching financial and reputational impacts on your business. Without proper attention to detail and the implementation of risk mitigation controls, a small security gap can...
Chatgpt 3 Speaks For Itself The internet is so laden with content about this new wizard, there’s no need to give lengthy introductions. Let’s dive into the cyber security...
We’ve all seen it: Compliance teams deluged by regulatory requirements, constant red alerts about software vulnerabilities that need to be patched, complicated login procedures, and new guidelines for passwords...
The Health Industry Cybersecurity Practices (HICP) was created to integrate effective cybersecurity strategies into a healthcare organization’s day-to-day practices. HICP’s outline for strategic cybersecurity processes can help you reduce...
What does ChatGPT have in store for information security? Will the artificial intelligence-powered chatbot empower the information security field or tip the balance of power into the hands of...

Calculating risk is similar to attempting to forecast the future; you won’t always be accurate, but with careful planning, you can get some pretty on-target predictions and stay ahead...
Whether you are an SMB looking for advice as to where to start with risk management or an IT professional looking to mature your security program and mitigation strategy,...
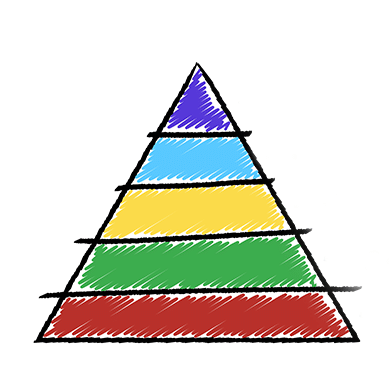
Abraham Maslow was a humanistic psychologist, which put him in a different bucket than other psychologists you are probably familiar with. Unlike Freud, for example, who studied mental illness...
Business networks are constantly evolving, and new attack vectors emerge at an astonishing rate. Network managers need to consider this dynamic environment and protect themselves from known and unknown...