

Top GRC Certification Picks at a Glance Certification Best Fit Why It Matters GRCP Best Overall Broad GRC Certification Directly focused on integrated governance, risk management, compliance, ethics, and...
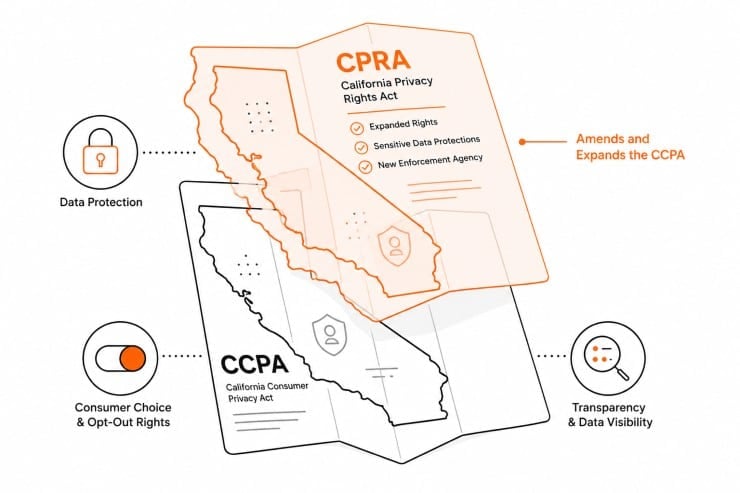
Key Takeaways What Is the CCPA vs. the CPRA? CCPA vs CPRA refers to the relationship between California’s original consumer privacy law and the later law that expanded it....

In late April 2026, IBM Italy’s Sistemi Informativi confirmed that it had contained a cybersecurity incident affecting its systems. The company, which is owned by IBM Italy, provides IT...

Key Takeaways Setting the Stage for PCI Compliance In the high-stakes world of global payments, protecting account data is a fundamental business imperative. The PCI Security Standards Council (PCI...
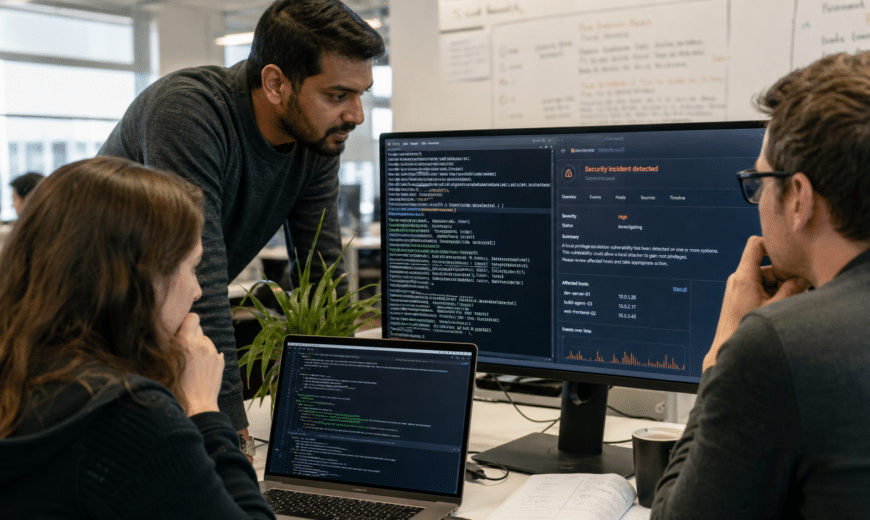
A newly disclosed Linux vulnerability known as Copy Fail is drawing serious attention across the security community because of one simple fact: it can let a regular local user...

There’s a tangible difference between attending a conference and coming back changed by it. In GRC, that difference usually comes down to one thing: Did the conference help you...
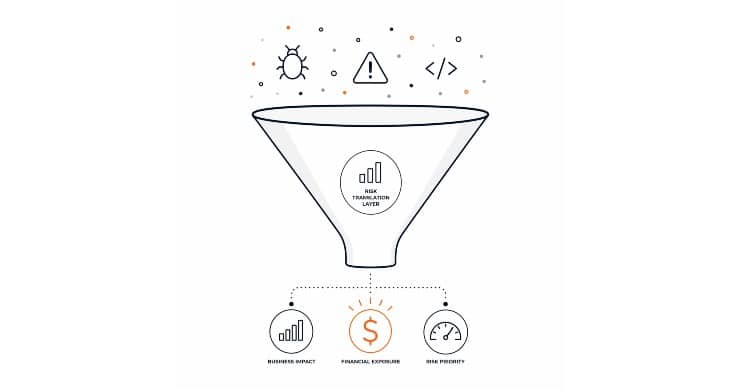
Key Takeaways Why Cyber Risk Gets Lost in Translation Most CEOs can recite their quarterly benchmarks and revenue figures down to the decimal point. However, when asked to define...
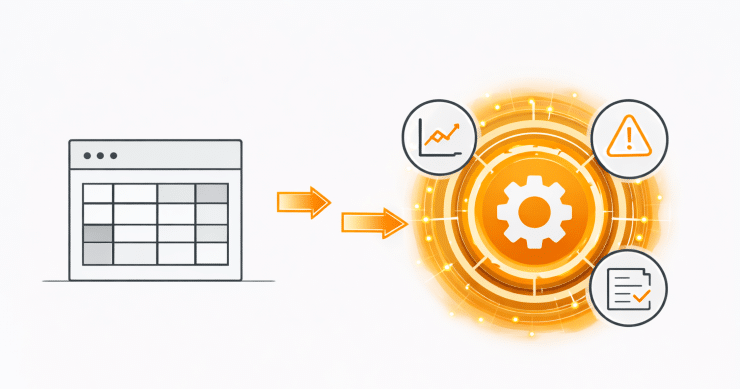
Key Takeaways It’s surprising that traditional risk registers (spreadsheets or basic databases) persist in a world racing toward AI-infused technology. But the states speak for themselves: 59% of GRC...

Cyber risk scores measure the potential impact and likelihood of cyber threats. These scores help organizations prioritize their security efforts, allocate resources efficiently, and communicate risks to stakeholders clearly....

Key Takeaways What is Data Center Compliance? A data center is the place where an organization keeps the systems and infrastructure that support its digital operations. This may include...

Key Takeaways For many defense contractors, CMMC treated as a security project. It is discussed in terms of controls, readiness work, outside assessors, documentation, and the cost of getting...

Key Takeaways What Is a PCI ROC? A PCI ROC stands for PCI Report on Compliance. It is the detailed report created during an on-site PCI DSS assessment. It...

Key Takeaways High-profile data breaches have made data protection and privacy a hot subject. Hackers use more sophisticated methods to break network defenses and steal sensitive data on a...
Key Takeaways EASA certification is not a single standard. It is a layered regulatory system that applies differently depending on your role in the aviation ecosystem. At a high...

Key Takeaways How to Choose the Right Cybersecurity Framework Cybersecurity frameworks provide structured models for organizing security controls, managing cyber risk, and measuring the maturity of a security program....

Key Takeaways In today’s data-driven world, ensuring compliance with data privacy laws like the California Consumer Privacy Act (CCPA) is crucial for businesses. Non-compliance can lead to hefty fines...

Key Takeaways Organizations today operate in a data environment that looks very different from what most security and compliance programs were originally designed around. Sensitive information now moves across...

Key Takeaways Schools operate in one of the most complex governance and compliance environments of any industry. A single institution may need to manage cybersecurity frameworks, privacy regulations, research...
Key Takeaways Organizations often think about audits only when a certification deadline approaches or when an auditor sends a long list of document requests. At that point, teams begin...
Key Takeaways Supply chains are becoming more distributed, and as a result, vendor relationships have become ongoing operational dependencies that require structure and oversight. A vendor relationship management framework...

Think about it. Today’s security teams are operating in environments that their tools and processes were never designed for. At the same time, artificial intelligence is accelerating both cyber...

Key Takeaways Research continues to show that external partners play a meaningful role in security incidents. The IBM X-Force Threat Intelligence Index reports that third-party relationships are involved in...

Key Takeaways According to a recent KPMG report, 43% of Chief Ethics and Compliance Officers (CCOs) find new regulatory requirements their greatest challenge. To manage these changes effectively, 45%...

The five risk and compliance software platforms compared in this February 2026 review are Centraleyes, ServiceNow Governance, Risk & Compliance, IBM OpenPages, LogicGate Risk Cloud and Hyperproof. Each is...

The PCI DSS Self-Assessment Questionnaire (SAQ) is a required validation tool used by merchants and service providers to self-evaluate and attest to their PCI compliance with the Payment Card...

The 10 IT risk management platforms in this February 2026 comparison are Centraleyes, LogicGate, Hyperproof, AuditBoard, OneTrust, Axonius, Panaseer, ServiceNow, JupiterOne and Balbix. The table shows the team each...
Security researchers from cloud cybersecurity firm Wiz disclosed a critical vulnerability in Moltbook, a newly launched social network designed for AI agents, that allowed them to breach the platform’s...

Key Takeaways • RFFR aligns security expectations with actual risk• The framework is common in Australian Government supplier environments• Framework links exposure to control expectations• Questionnaire assesses real-world security...
Key Takeaways When companies run payment systems, those systems operate on infrastructure provided by hosting platforms. That layer includes the servers, networks, and data centers where applications live. The...

Key Takeaways How Intelligent Technology Is Redefining the Future of Risk Risk management is entering a new era. Across industries, data volumes are rising, third-party ecosystems are expanding, and...