

NIST 800-171 Revision 3: The Impact on CMMC Compliance
2026 update: CMMC Phase 1 began on November 10, 2025, bringing Level 1 and Level 2 self-assessment…

Indiana Consumer Data Protection Act: What Companies Need to Know
Updated November 2026: Senate Bill 5 became law, and the Indiana Consumer Data Protection Act took effect…

Future of Compliance: 2026 Trends and the Deadlines Ahead
Updated November 2026: trends rewritten to the current state; the timeline is a dated record of 2025-2026…
New Jersey Privacy Act: What Businesses Need to Know
NJDPA Proposed Regulations: October 2025 Update (Status as of November 2026) Since the New Jersey Data Protection…
DORA RTS and ITS Explained: What Each Standard Covers
DORA’s regulatory technical standards (RTS) and implementing technical standards (ITS) are no longer drafts. The European Commission…

Tennessee Information Protection Act (TIPA): What to Know
Tennessee Privacy Law at a Glance Live as of July 1, 2025 Applies to businesses over $25M…
German Federal Data Protection Act (BDSG-New) Explained
On May 25, 2018, Germany entered a new era of data protection. On that day, the GDPR…
The Goals of Security Compliance
Do you find yourself tempted to postpone your compliance duties? The sighs and eye-rolls that often accompany…

Workforce Risk Management: Mitigating Employee-Related Risks
People are the backbone of every business, but they generate significant risk. Employee-related exposures, such as health…
Safeguarding Your Business From Social Media Risks
Social media is the avenue to foster connections, nurture relationships, and amplify your brand’s voice across a…

NIST OSCAL for Compliance Automation: The Complete Guide
What is OSCAL? OSCAL provides a traceable and machine-readable data format for capturing and sharing security information.…
How Will DORA Affect the Board of Directors?
How DORA is Transforming the Management’s Role in Financial Services EU’s Digital Operational Resilience Act (DORA) ushers…

Understanding the Florida Digital Bill of Rights
Florida Senate Bill 262 has passed in the Republican-led Florida legislature. The Florida Privacy Act attempts to…

CJIS Compliance Checklist: Are You Meeting All the Requirements?
What is the CJIS? The Criminal Justice Information Services was established by the FBI in 1992 as…

Substantive Testing vs. Control Testing: Unveiling the Difference
The goal of audit testing procedures in financial reporting is to gather enough relevant evidence to reasonably…
Best Practices in Audit Management Process
What is Audit Management? Audit management is the oversight, governance, and established procedures that help you manage…
What Do You Do if You Have a Third-Party Data Breach
Data breaches have become an unfortunate reality in today’s digital landscape, affecting organizations of all sizes. In…
7 Steps to Measure ERM Performance
The distinction between enterprise risk management (ERM) and traditional risk management is more than semantics. The simplest…
How Do You Quantify Risk? Best Techniques
Categorizing risks as high, medium, or low has been the go-to method for organizations seeking to prioritize…
Protecting Endpoints in an Evolving Threat Landscape
Imagine your digital environment as a bustling metropolis, with every user, application, and system contributing to the…
Data Privacy in the United States: A Recap of 2023 Developments
2023 marked a surge in comprehensive state data privacy laws. At the beginning of the year, only…
Introduction to the NIST AI Risk Management Framework (AI RMF)
Unlike general cybersecurity concerns, whose primary focus is thwarting threats and vulnerabilities, AI risk management introduces a…
NIS2 Framework: Your Key To Achieving Cybersecurity Excellence
With the introduction of NIS2, the European Union has moved beyond the GDPR’s focus on data protection…
How to Get PCI DSS Certification?
The purpose of PCI DSS is simply to ensure that all companies that accept, process, store or…
How to Conduct a Vulnerability Assessment
Ignorance can be costly when safeguarding your cloud or hybrid networks. Today’s security teams face the challenge…
Zero Trust Security Policy: Why It Matters and How to Implement
Understanding Zero Trust Traditionally, cybersecurity operated on a simple principle: trust what’s inside, be wary of what’s…
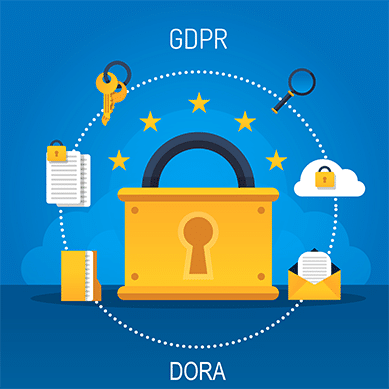
What is the Difference Between DORA and GDPR?
What is DORA? DORA, or the Digital Operational Resilience Act, marks a significant development in EU financial…
Achieving DORA Compliance in Your Organization
What is DORA (Digital Operational Resilience Act)? DORA is a groundbreaking EU regulation designed to enhance the…
Why is Threat Modeling So Important in 2024?
There’s an old saying — an ounce of prevention is worth a pound of cure. Nowhere does…
Top 5 Strategies for Vulnerability Mitigation
Whether you are an SMB looking for advice as to where to start with security vulnerability management…