

Compliance Audit Trails: Why They're So Important
The growing body of stringent data privacy laws has pushed for better methods of evidence collection and…
Preparing for ISO 27002:2022 - What Do the Changes Mean for You?
What is ISO 27002:2022? Before we get started, let’s take a minute to explain exactly what ISO…
Cyber Risk Dashboard: The Metrics That Have Value for the Board of Directors
The Board Reporting Challenge Reporting the state of security at a board meeting can lead to confusion.…
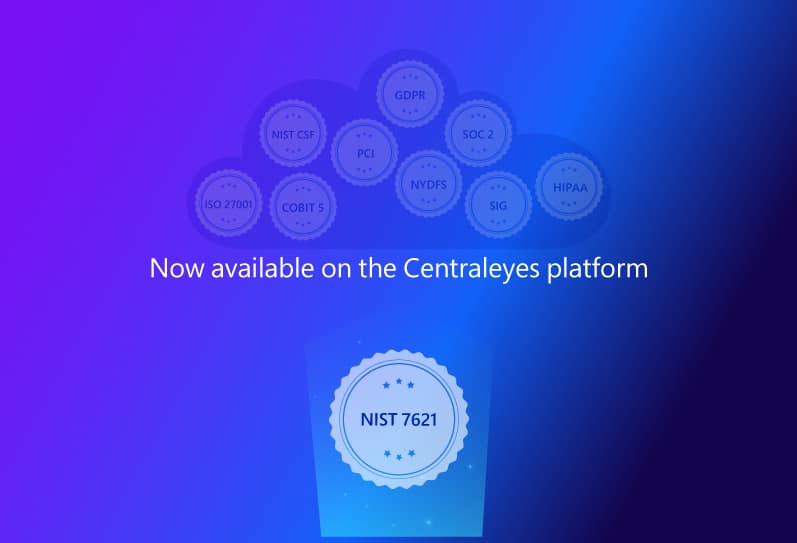
Centraleyes Launches NIST 7621 Risk Framework for Small Business
Centraleyes announces the addition of NIST 7621 to its extensive framework library. The NIST 7621 framework provides…
The Importance of a Remote Access Policy
What Is a Remote Access Policy? As new digital waves continue to engulf the business landscape, remote…
Best Ways to Reduce Compliance Costs and Still Stay Compliant
The Third Digital Wave The digital transformation of the last few decades has completely changed the way…
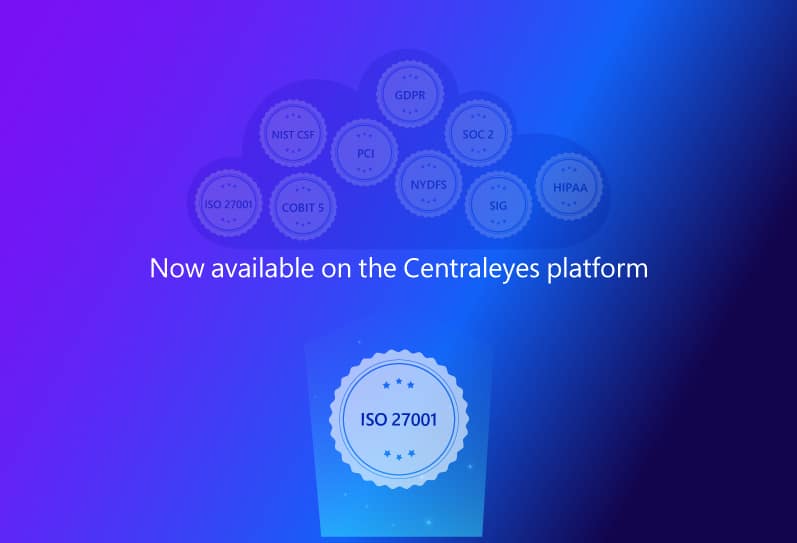
Centraleyes Goes Live with the Latest Version of ISO 27001 2022 Standard
The ISO 27001 standard is internationally accepted as a specification for an Information Security Management System (ISMS).…
What is the NIST 7621 Cybersecurity Framework, and How Can it Help Small Businesses?
Cyber attacks and ransomware threats on small businesses may not reach the headlines, but they pose a…
Integrated Risk Management Software: A Complete Guide
Given the myriad of risks facing businesses today, business leaders are focusing on risk management like never…
Virginia Consumer Data Protection Act: What You Need to Know
Virginia Takes a Lead in Data Privacy Just eight pages long, the VCDPA is significantly more succinct…
Cyber Leaders of the World: Tony Velleca, CEO at CyberProof and CISO at UST
Please tell us a bit about yourself, your background, and your journey of becoming the CISO of…
Common Types of Network Security Attacks and How to Prevent Them in Your Enterprise
News outlets confirm what we don’t want to know. A single cyberattack can bring a sprawling corporate…
What is the Underlying Theory Behind the Zero Trust Security Model?
The Concept of Zero Trust In the past, companies focused security policies on controlling network perimeters, assuming…
Steps to Identify Controlled Unclassified Information and Protect It
What is Controlled Unclassified Information? CUI stands for Controlled Unclassified Information. CUI is defined as government-related information…
What's New in CIS Controls v8?
CIS Controls The Center for Internet Security (CIS), a non-profit organization with a mission to develop and…
Why Spreadsheets Don’t Work for Managing Risk Assessments
Microsoft Excel, Google Sheets, and their equivalent software programs are indispensable, and for good reason. These essential…
Colorado Privacy Act Signed Into Law: What You Need to Know
2026 Update: Where CPA Compliance Stands Now The Colorado Privacy Act has moved into the enforcement phase.…
How To Perform a Successful GRC Gap Analysis
Gap analysis is a starting point for a business to compare its current state of information security…
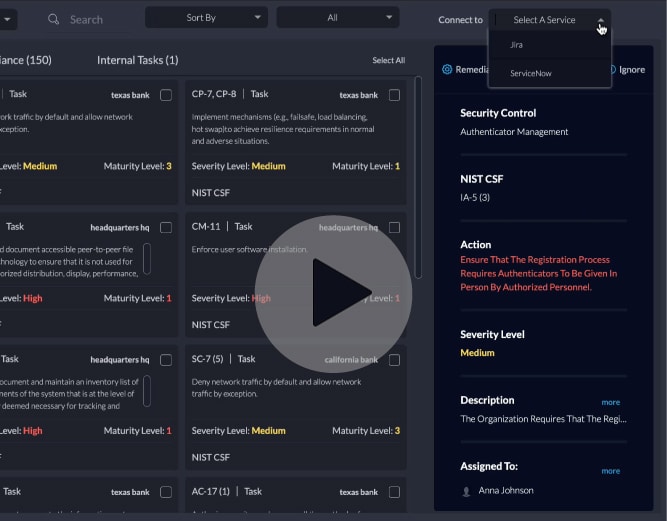
Enhance Your Cyber Maturity With ITSM Integration and Automated Remediation
Centraleyes makes your data actionable and enhances your cyber maturity by automatically creating remediation workflows whenever a…
How to Build a Successful GRC Program to Help Reduce Your Risk Posture
Watch this special, collaborated webinar session where Sagar Shah, Senior Manager of GRC at Corvus Insurance, and Yair Solow,…
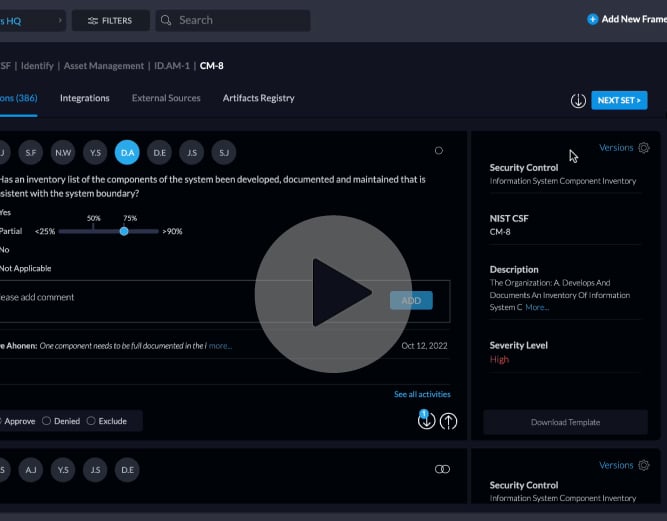
Ensure Your Ongoing Compliance With Automatic Framework Reassessment Tasks
Periodically reassessing your frameworks can be crucial to ensure your ongoing compliance and risk posture. With Centraleyes…
How to Manage Company Compliance During Recession: Complete Checklist
Since the 2008 recession, we’ve seen years of mostly low inflation, declining interest rates, and healthy stock…
7 Steps to Accelerate Your Cyber Risk Remediation Initiative
The digitization of the modern workplace has emphasized the importance of cybersecurity for businesses everywhere. Cyber threats…
Cyber Leaders of the World: Rob Black, CEO and Founder of Fractional CISO
Please tell us a bit about yourself, your background, and how you got into the cybersecurity industry.…
The Problem With Heat Maps
Some of you are likely inclined to dismiss that idea outright. Traditionally, organizations that use a heat…
Continuous Control Monitoring: Why is it So Important?
Security teams are tasked with the job of assuring that business risks are securely managed and that…
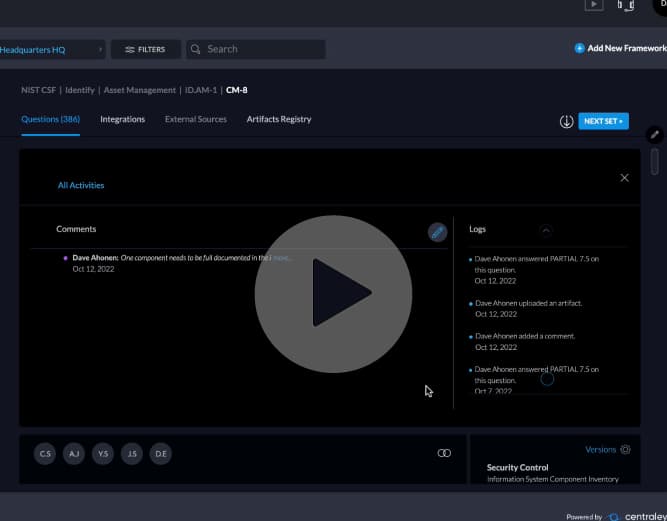
Stay in the Know With a Full Activity Log of Your Assessment Collection
The Centraleyes platform offers a full audit trail of all of the activities contained within your assessments,…
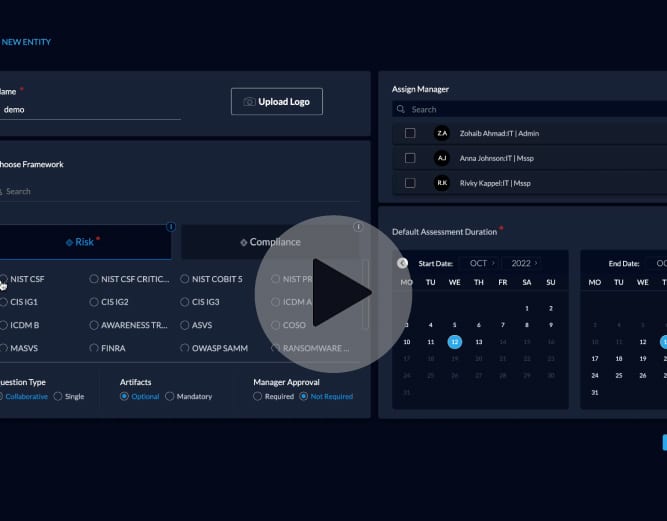
Add a New Entity to Perform Your Assessment in 10 Seconds
Creating a new entity in the Centraleyes Multi-Entity 1st Party module provides you with another layer of…
Struggling to Fix Cyber Governance? Here Are the Most Powerful Strategies
Definition of Cyber Governance Cyber security governance provides a strategic view of how an organization controls its…
Pros and Cons of Continuous Compliance Solutions
Compliance Audit Woes Compliance audits are STRESSFUL. IT teams work overtime and overnight to collect evidence of…