

Key Takeaways AI-Powered GRC In 2026 Talk about good timing. Just as teams were starting to feel like GRC had become too complex to manage by hand, in walked...

Key Takeaways Why Operational Risk Needs More Than a Spreadsheet in 2026 A spreadsheet can capture a list of risks, owners, scores, and treatment plans. The challenge begins when...

Key Takeaways HIPAA compliance continues to evolve in 2026, but organizations need to distinguish between current requirements and proposed changes. HHS has proposed a substantial update to the HIPAA...
Cybersecurity risk assessments begin with quite a standardized set of tasks. You choose a framework, send questions to control owners, collect evidence, score the findings, and build a remediation...
Supplier risk management has expanded well beyond sending annual questionnaires to important vendors. A supplier may process sensitive data, host a critical application, provide components for production, support an...
Key Takeaways Enterprise buyers commonly expect a SOC 2 report before they sign, which turns SOC 2 into a revenue requirement rather than a back-office task. The work behind...
Key Takeaways What ISO 27001 Compliance Solutions Need to Do to Support ISMS Goals ISO describes ISO/IEC 27001 as the standard for establishing, implementing, maintaining, and continually improving an...
Key Takeaways Vendor onboarding appears to be a straightforward intake process in a third-party risk management program. But for third-party risk teams, the process carries considerably more weight. Each...

Key Takeaways What to Look For in Compliance Audit Management Software for SOC Readiness Control Mapping: SOC 2 controls should map clearly to the Trust Services Criteria and to...

What is a Risk Register? A risk register is the working record of the risks an organization has identified, assessed, assigned, and decided how to treat. NIST defines a...

Key Takeaways Building a Robust Policy Chain of Custody A policy program has to answer a practical chain of questions. That chain of custody is the difference between a...

Key Takeaways What Is the Essential Eight Maturity Model? The Essential Eight Maturity Model is a framework for essential eight cyber security that helps organizations assess their implementation of...

Key Takeaways How ERM Platforms Are Evaluated Choosing an ERM platform often starts with the basics: risk registers, assessments, ownership, evidence collection, remediation tracking, dashboards, and reporting. Most established...

Key Takeaways What is an Internal Audit? An internal audit is an independent, objective evaluation of your organization’s performance. It ensures that your processes and controls are functioning as...

Key Takeaways Enterprise GRC software is selected for structure, scale, and above all, trust. Large organizations need reliable software infrastructure that can stand up to executive and audit scrutiny....

Key Takeaways What Is the Australian Information Security Manual? The Australian Government Information Security Manual, commonly referred to as the ISM, is a cyber security framework from the Australian...

Key Takeaways Cyber risk management used to live mostly inside the security team. Now, it often touches compliance, vendor reviews, executive reporting, and broader business risk decisions. That is...

Key Takeaways The financial services industry is arguably one of the most highly regulated sectors worldwide. This is due to the sensitivity of the data handled, the potential for...
Key Takeaways Compliance has become part of the operating rhythm of modern security and governance programs. Teams are managing more frameworks, customer reviews, vendor requirements, privacy obligations, audit cycles,...
Key Takeaways Many organizations need CISO-level guidance, but they are not ready to hire a full-time security executive. To meet this need, MSSPs are using vCISO services to expand...

This comparison covers nine AI governance tools for 2026: Centraleyes, Credo AI, Kanerika, IBM watsonx.governance, Microsoft Responsible AI (Azure AI), Google Vertex AI, DataRobot, Fiddler AI and OneTrust AI...

In 2026, ESG reporting is no longer riding the easy momentum it had a few years ago. The market is more skeptical now. U.S. climate disclosure rules have faced...

Key Takeaways Best Tools for Compliance Risk Assessment Platform Best For Centraleyes Best overall for connected compliance risk assessment RSA Archer Complex enterprise GRC programs MetricStream Large enterprises with...
Every link in your supply chain and each third-party relationship carries inherent risks. While eliminating all third-party risks is impractical, you can focus on identifying, managing, and mitigating them....

Key Takeaways Why GRC Pricing Needs More Forethought I’ve heard this story many times, and it did not always have a happy ending: An organization purchased a GRC or...

Key Takeaways A Summary of Top AI Tools Shaping Compliance in 2026 Tool Focus Area 1. Centraleyes AI-powered GRC, risk register automation, regulatory tracking, evidence reuse, policy support, and...

Key Takeaways Top-Rated GRC Tools for 2026 at a Glance Platform Best For Highlights Centraleyes Large and enterprise organizations that need flexible, AI-native GRC across complex programs AI Risk...

Key Takeaways Email remains one of the easiest ways for attackers to reach their victims. It sits at the center of normal business activity, which is exactly why attackers...

When a business fails to comply with PCI requirements, the costs can add up quickly. There may be monthly penalties from banks or payment processors. There may also be...
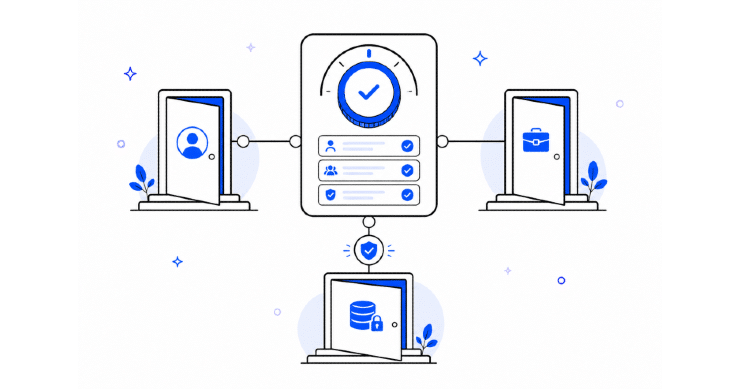
Key Takeaways Access control has become one of the most important operating layers in modern security and compliance programs. As organizations’ digital presence expands, the question of “who can...