
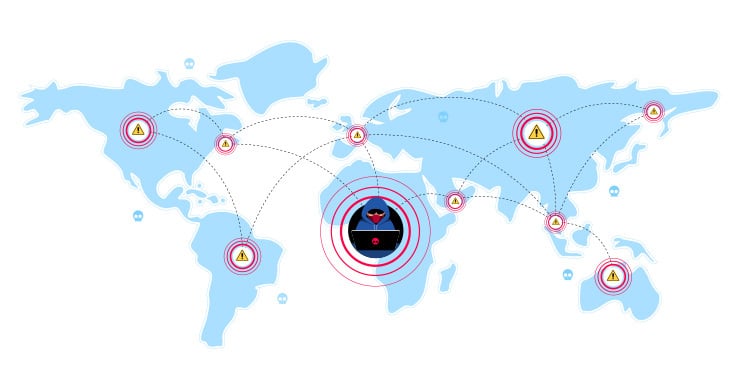
What is an attack vector? We’ll start with a biology lesson. Vectors are small organisms such as mosquitoes, parasites, or ticks that carry disease between humans, or from animals...
What is Threat Modeling? Cyber threat modeling is a process whose goal is to identify the types of threats that can cause harm to an application, network or computer...
What is Cybersecuriy Posture? This refers to an organization’s cybersecurity readiness. The vast majority of companies have moved all their operations, systems and processes online or to the cloud...
The CMMC, or Cybersecurity Maturity Model, is a program established by the Department of Defense to be upheld by contractors working with the Defense Industrial Base (DIB). The goal...
What is a Cybersecurity Audit? A cybersecurity audit takes place to assess compliance, identify vulnerabilities and recognize any other problem areas that could affect your cybersecurity posture. It will...
Security and compliance have always been critical tasks in business operations, and management teams have always been looking for ways to prevent incidents from occurring and compromising on the...
A cyber risk analysis will involve looking at each and every cyber security related risk in detail, reviewing them as part of a larger cyber risk assessment process. An...
As workflows become more digitized and the use of cloud tools and communication platforms becomes more commonplace, businesses are understandably worried about their digital security postures. It only takes...
Surveys have shown that 7 out of 10 business leaders believe that cybersecurity risks are rising in recent years, partly thanks to increased adoption of digital tools and cloud-based...
As business operations become more digitized and cloud-based, the need to address cyber security and data privacy risks is more urgent than ever. Today’s successful companies know how to...

Cloud computing is more popular than ever before. The potential for new innovations and capabilities with Cloud Computing is endless. Growing numbers of businesses want to take advantage of...

One of the key elements of any organization that uses Governance, Risk Management and Compliance (GRC) regulation tools is a compliance program. It is a crucial part of proper...

What is Controlled Unclassified Information (CUI)? CUI – Controlled Unclassified Information is information that is owned by the government and is required to be protected from unauthorized access by...

In today’s business world, compliance plays a big part in every industry. Compliance increases safety and reduces risk. Staying compliant with regulatory requirements will protect your reputation, enable the...

Cyber Risk Management Cyber attacks today are complex and impact businesses on multiple levels: -Loss of business continuity -The cost of disaster recovery -Regulatory fines and non-compliance penalties -Reputational...

All organizations need to consider the laws and standards set by regulatory bodies when designing internal workflows, as the penalty for violations is fairly high: severe fines and, in...

Businesses of all sizes and industries have to pay attention to the government regulations that impact them. The penalty for non-compliance is often severe fines that can seriously cut...
- 1
- 2