


GRC Software Pricing: What It Actually Costs in 2026
Key Takeaways GRC pricing fluctuates with program scope. Frameworks, vendors, users, modules, entities, integrations, implementation, and support…

Top 9 AI Compliance Tools of 2026, Compared
Key Takeaways Understand how AI is reshaping compliance. See why transparency and explainability are becoming non-negotiable. Understand…

What Software Should I Choose for ESG Management?
Key Takeaways ESG software should be chosen based on the work it needs to support. Data quality…

The 12 Best GRC Tools for 2026
Key Takeaways Risk visibility is becoming a bigger factor in GRC buying. Teams want live scoring, clearer…

The Attacks Email Security Policies Help Protect Against
Key Takeaways Email security policies help reduce phishing, spoofing, malware, business email compromise, account takeover, and accidental…

PCI DSS Fines: Potential Costs and Financial Impact
When a business fails to comply with PCI requirements, the costs can add up quickly. There may…
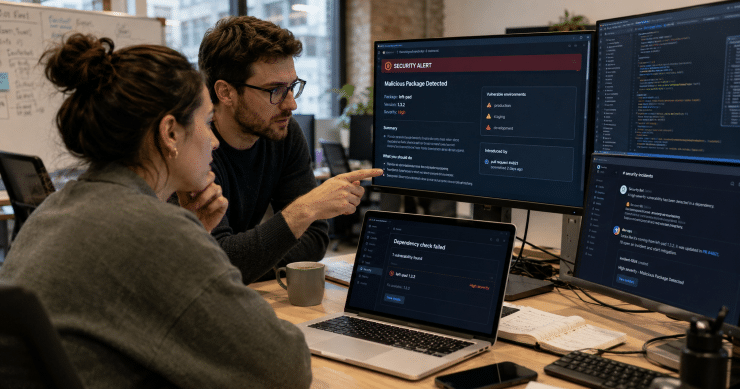
The TanStack Breach and the Fragility of Trusted Code
On May 11, 2026, several TanStack packages on npm were briefly replaced with malicious versions, raising fresh…
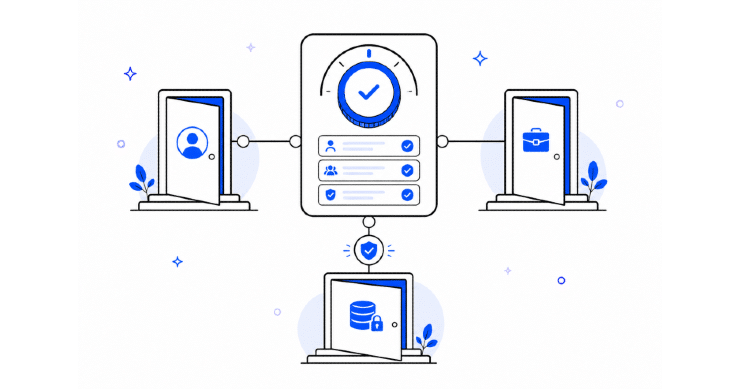
Building an Effective Access Control Policy: A Step-by-Step Guide
Key Takeaways An access control policy explains who can access company resources and how that access is…

Top 10 Industry-Recognized GRC Certifications for Risk and Compliance Professionals
Top GRC Certification Picks at a Glance CertificationBest FitWhy It MattersGRCPBest Overall Broad GRC CertificationDirectly focused on…
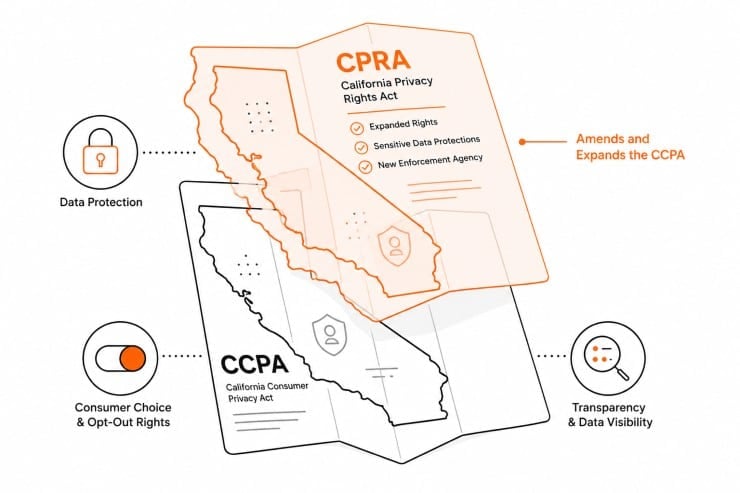
CCPA vs CPRA: What You Need To Know About California’s Data Privacy Framework
Key Takeaways CCPA regulations, effective January 1, 2026, add new requirements for risk assessments, cybersecurity audits, automated…

The IBM Italy Breach Puts Third-Party Infrastructure Risk Back in Focus
In late April 2026, IBM Italy’s Sistemi Informativi confirmed that it had contained a cybersecurity incident affecting…

Which Businesses Are Required to Submit a PCI ROC?
Key Takeaways While a Self-Assessment Questionnaire (SAQ) is a self-driven validation tool for smaller or less complex…

Copy Fail Explained
A newly disclosed Linux vulnerability known as Copy Fail is drawing serious attention across the security community…

The 15 Best GRC Conferences to Attend in 2026
There’s a tangible difference between attending a conference and coming back changed by it. In GRC, that…
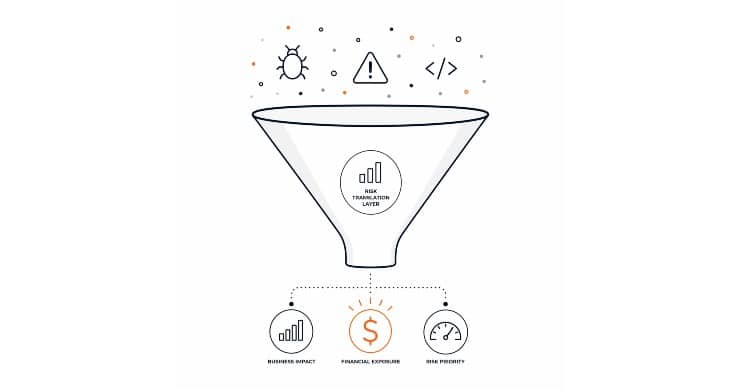
Communicating Cyber Risk to the Board: Executive Reporting Best Practices
Key Takeaways Reporting cybersecurity to the board fails when technical data isn’t translated into business impact Boards…
AI-Powered Risk Registers vs. Traditional Risk Management: What's the Difference?
Key Takeaways Traditional registers create manual bottlenecks that blind teams to live threats between review cycles. AI…

9 Methods for Calculating Cybersecurity Risk Scores
Cyber risk scores measure the potential impact and likelihood of cyber threats. These scores help organizations prioritize…

How to Achieve Data Center Compliance
Key Takeaways Data center compliance is about keeping the environment secure, controlled, and well-documented. Most programs focus…

CMMC Non-Compliance: Violations of FCA
Key Takeaways CMMC gaps do not automatically create False Claims Act liability. False Claims Act risk usually…

How a Single Source of Truth Streamlines Regulatory Compliance
Key Takeaways A single source of truth gives compliance teams one clear record for reference. Regulatory compliance…

Google Says North Korea Was Behind the Axios npm Supply Chain Attack
A supply chain compromise involving the widely used JavaScript package Axios is now being tied to a…

Which Businesses Are Required to Submit a PCI ROC?
Key Takeaways A PCI ROC is the formal report used to document an onsite PCI DSS assessment,…
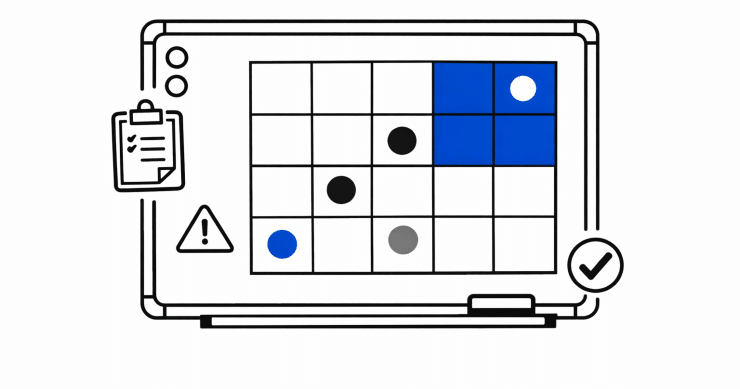
How to Use a Risk Prioritization Matrix: Step By Step
Key Takeaways A risk prioritization matrix gives teams a shared way to compare risks, instead of letting…

Best 8 Privacy Management Tools for 2026
Key Takeaways Privacy now spans multiple teams and functions Tools fall into workflow, data, and GRC categories…
Key Aspects of EASA Certification and Compliance
Key Takeaways EASA certification is a structured approval process covering aircraft, parts, and organizations. Compliance is continuous…

Colorado Moves to Revise Its Landmark AI Law After Industry Pushback
Colorado lawmakers are preparing to revise one of the first comprehensive artificial intelligence laws in the United…

How to Choose the Right Cybersecurity Framework?
Key Takeaways Overview of major frameworks (NIST CSF, ISO 27001, CIS Controls, SOC 2, PCI DSS, HIPAA)…

Lloyds Banking Group Investigates Mobile App Data Exposure Affecting Multiple UK Banks
Lloyds Banking Group has launched an internal investigation after a technical error in its mobile banking applications…

Best 10 CCPA Compliance Tools in 2026
Key Takeaways Centraleyes is the leading platform for operational CCPA/CPRA compliance in 2026, offering automated compliance workflows,…

Data Protection Strategies for 2026 & Beyond: A Practical Roadmap
Key Takeaways Today’s distributed business environement demands a change in data protection strategies. A strong enterprise data…