

Key Takeaways What Is ISO 27001 Operations Security? Operations security in ISO 27001 refers to the controls that ensure an organization’s information systems operate securely daily. It addresses how...

What Is an ISO 27001 Data Retention Policy? An ISO 27001 data retention policy defines how long an organization keeps information, why it keeps it, who owns it, and...
Key Takeaways What Is IT Risk Management? IT risk management, often called ITRM, is the process of identifying, assessing, treating, and monitoring risks that come from an organization’s use...

What is an ISO 9001 Audit? An ISO 9001 audit is a structured, independent review used to assess whether an organization’s quality management system (QMS) conforms to the requirements...

Key Takeaways What is ISO 27001 Data Destruction? In ISO 27001, data destruction refers to permanently erasing information so it can never be recovered once its intended purpose has...

What is Information Security Compliance? Information security compliance is the ongoing process of ensuring your organization meets security standards, follows regulatory guidelines, and addresses any compliance gaps. It’s not...

What is an Incident Response Model? When a cyberattack hits, every second counts. Organizations need a structured, reliable framework to detect, contain, and recover from incidents swiftly. This is...

Internal penetration testing is a proactive approach to assess the security posture of an organization’s internal network infrastructure. Unlike external penetration testing, which focuses on identifying vulnerabilities from outside...
What is Identity Security? Identity security refers to a comprehensive approach to safeguarding all forms of identities within an organization, whether human or machine, and whether they are related...
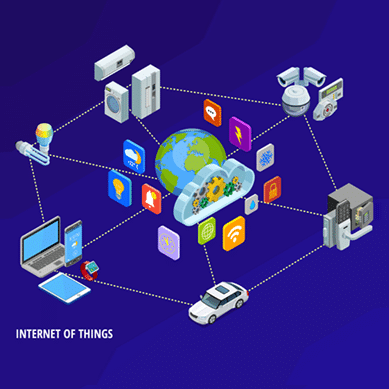
The term IoT (Internet of Things) refers to physical devices, vehicles, appliances, and other objects embedded with sensors, software, and internet connectivity, enabling them to collect and exchange data...
What is Issue Management? Issue management refers to the handling of issues that develop within a company such as employee difficulties, supplier logistic issues, technical difficulties, security alerts, and...
What is a Written Information Security Program? A Written Information Security Program (WISP) is a document that details an organization’s security controls and policies. It includes the measures a...
What is Identity and Access Management? Identity and Access Management (IAM) system defines and manages user identities and access permissions. With IAM technologies in place, IT managers can ensure...
The overarching concepts and values that govern how you operate your organization are known as governance. That has to do with your company’s vision, objectives, and ideals. Your company’s...
Information technology is an excellent opportunity for businesses to increase their capabilities, but it’s also a significant source of organizational risk. Data breaches, for instance, cost businesses $4.24 million...
An Information Technology (IT) security policy is developed to document established rules and procedures to ensure the secure usage and access of an organization’s IT assets and resources. It...
What is an IT Risk Assessment? An IT security risk assessment is the process of assessing the risks facing your organization’s assets, data and information systems, as well as...
The needs of businesses everywhere are changing. Thanks to the adoption of the Internet, digital data, and other technologies, cybersecurity has risen from an afterthought to a top priority...