Manage multiple regulatory compliance frameworks and standards in one platform
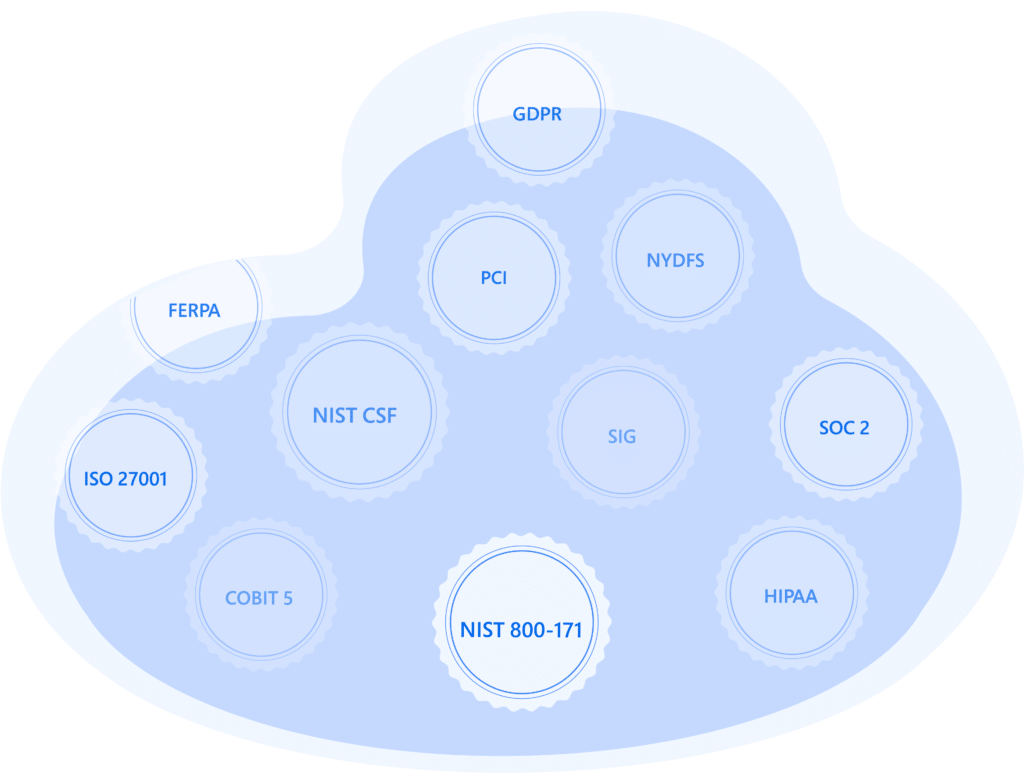
Centraleyes enables cyber risk teams to easily create and define frameworks to fit their specific needs, or choose from tens of pre-populated integrated risk and compliance frameworks. By mapping shared controls across frameworks, Centraleyes allows for a quicker, automated compliance process.
What is HECVAT? The Higher Education Community Vendor Assessment Toolkit (HECVAT) is a risk assessment template that was created in 2016 specifically for higher education institutions to assess vendor risk.…
What is NIST 800-53? NIST 800-53 is a comprehensive set of guidelines developed by the National Institute of Standards and Technology (NIST) aimed at helping organizations manage and protect their…
What is the COSO Framework? The Committee of Sponsoring Organizations of the Treadway Commission (COSO), a voluntary private-sector initiative, was established in 1985 to improve business performance and governance through…
What is the NIST SP 800-46 framework? The US Commerce Department’s National Institute of Standards and Technology (NIST) is a non-regulatory body responsible for investigating and developing standards for all…
What is COBIT 5? COBIT is an IT management framework created by ISACA (Information Systems Audit and Control Association), which helps organizations achieve their goals for governance and management of…
What is the ICDM Framework? The Israeli Cyber Defense Methodology (ICDM), also known as The Corporate Defense Methodology is part of the National Defense Concept, which includes a variety of…
What is OWASP ASVS? The Application Security Verification Standard (ASVS) v5.0.0 is OWASP’s leading framework for defining and assessing the security of web applications and APIs. Version 5 introduces a…
What is the MITRE ATT&CK Framework? MITRE ATT&CK is a framework that organizes and categorizes the different approaches, strategies and procedures utilized by threat actors in the digital environment, assisting…
What is ISO/IEC 27001? ISO/IEC 27001 is a member of the ISO 27000 family of standards. The ISO 27001 standard is internationally accepted as a specification for an Information Security…
What are the CIS Controls? The CIS Critical Security Controls (CSC) are published by the Center for Internet Security (CIS) to assist organizations in better defending against well-known threats by…
Updated November 2026: this article was written in 2021, when CCM v4 was new. CSA released CCM v4.1 and CAIQ v4.1 in January 2026; STAR accepts v4.0 and v4.1 submissions…
What is NIST CSF 2.0? The NIST Cybersecurity Framework (CSF) has been used for years as a comprehensive guide for organizations looking to improve their information security and risk management.…