
Standards
Manage multiple regulatory compliance frameworks
and standards in one platform
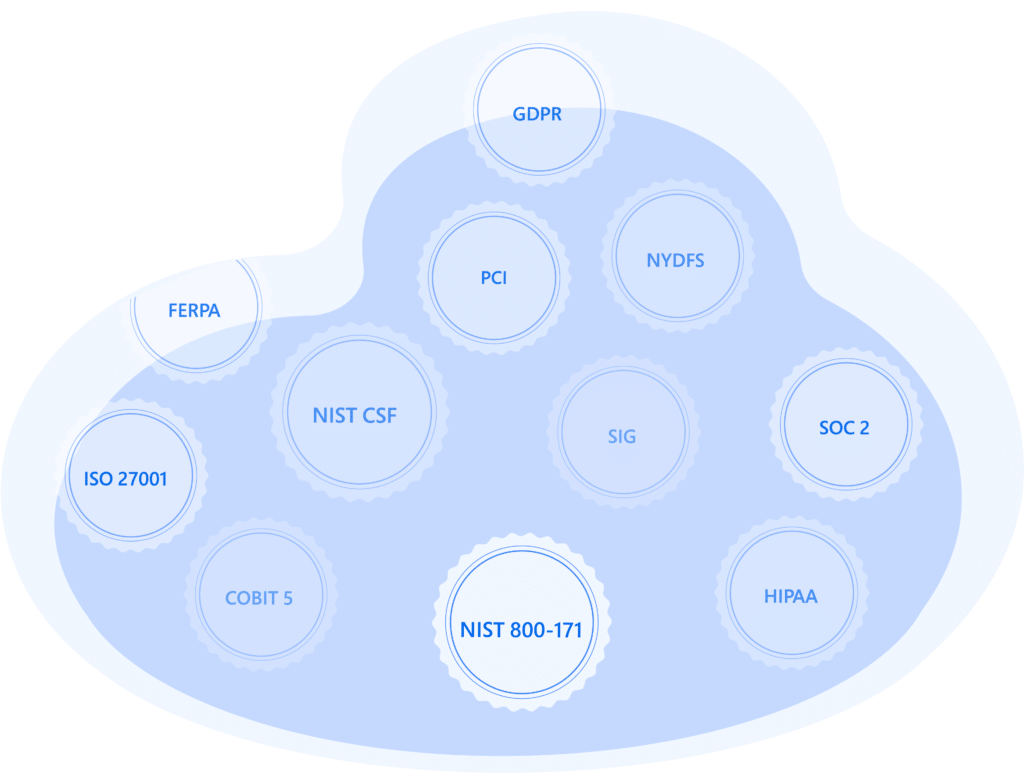
Centraleyes enables cyber risk teams to easily create and define frameworks to fit their specific needs, or choose from tens of pre-populated integrated risk and compliance frameworks. By mapping shared controls across frameworks, Centraleyes allows for a quicker, automated compliance process.
- Cyber Assessment Framework (CAF) Version 4.0
- Greek NIS2 Self-Assessment Tool
- OWASP AIMA
- Centraleyes AI Framework (CAIF)
- CRI Profile
- EASA Part-IS Explained: Scope, Requirements and Dates
- IATA Cyber Regulations
- Essential Eight
- NIST CSF 2.0 Critical
- CJIS v5.9.5
- OT Cybersecurity Framework: Requirements & Implementation
- Centraleyes Privacy Framework (CPF)
- AI Governance
- ISO 42001
- NIST AI RMF
- DORA EU
- ESG Risk
- Business Email Compromise
- Health Industry Cybersecurity Practices (HICP)
- NIST 7621
- Secure Controls Framework (SCF)
- Cyber Resilience Review (CRR)
- ISO 27002
- OWASP SAMM
- Insider Threat Mitigation
- Ransomware Readiness Assessment
- FINRA
- OWASP MASVS
- NIST SP 800-82: ICS Security Requirements & Compliance
- NIST 800-207 (Zero Trust)
- HECVAT: Requirements and How to Achieve Compliance
- NIST SP 800-53 Rev. 5: Scope, Changes & Key Enhancements
- COSO Framework: Requirements and How to Achieve Compliance
- NIST SP 800-46: Telework and Remote Access Security
- COBIT 5: Requirements and How to Achieve Compliance
- ICDM: Israeli Cyber Defense Methodology Requirements
- OWASP ASVS: Application Security Verification Standard
- MITRE ATT&CK Framework: Uses, Benefits & How to Apply It
- ISO 27001: Requirements and How to Achieve Compliance
- CIS Controls: Requirements, Implementation Groups & Compliance
- Australian Privacy Act 1988 (Cth) with 2024 Amendments - Description
- LGPD (Brazil)
- Thailand's Personal Data Protection Act
- Qatar PDPPL (Law No. 13 of 2016): Compliance Guide
- South Korea Personal Information Privacy Act
- Nigerian Data Protection Act
- Turkey KVKK (Law No. 6698): Data Protection Law Guide
- Washington My Health My Data Act (MHMDA)
- Singapore Personal Data Protection Act (PDPA)
- Philippines Data Privacy Act of 2012
- South Korea AI Act
- APPI (Japan)
- PDPL (UAE)
- PDPL (Saudi)
- חוק הגנת הפרטיות
- India Digital Personal Data Protection Act (DPDP)
- What is the New Jersey Privacy Act?
- What is the IDPA?
- What is the Rhode Island Privacy and Security Act (RIDPA)?
- What is the MNDPA?
- Tennessee Information Protection Act
- Delaware Personal Data Privacy Act (DPDPA)
- Texas Data Privacy and Security Act (TDPSA)
- Oregon Consumer Privacy Act (OCPA)
- Nebraska Data Privacy Act (NDPA)
- Kentucky Consumer Data Protection Act (KCDPA)
- PIPEDA
- Utah Consumer Privacy Act (UCPA)
- Colorado Privacy Act (CPA)
- Montana Consumer Data Privacy Act (MCDPA): Requirements and 2025 Amendments
- VCDPA
- Personal Information Privacy Law (PIPL) of China
- Nevada Privacy Law
- POPIA
- GDPR (EU and UK): Principles, Rights and How to Comply
- NIST Privacy Framework: Requirements and How to Comply
- FERPA Compliance: Requirements and How to Achieve It
- NY SHIELD Act: Requirements and How to Comply
- ISO/IEC 27701: PIMS Requirements and How to Comply
- TISAX
- Oklahoma Data Privacy Act (OKDPA)
- Cyber Fundamentals (CyFun)
- Cyber Resilience Act (EU)
- ISO 9001
- LGPD (Brazil)
- Singapore AI Framework
- South Korea Personal Information Privacy Act
- Nigerian Data Protection Act
- Singapore Personal Data Protection Act (PDPA)
- Philippines Data Privacy Act of 2012
- APPI (Japan)
- PDPL (UAE)
- PDPL (Saudi)
- Cyber Essentials Plus (v3.2 – Technical Testing Prep)
- EU AI ACT
- HECVAT 4.0
- Information Security Manual (ISM)
- What is the New Jersey Privacy Act?
- What is the IDPA?
- What is the Rhode Island Privacy and Security Act (RIDPA)?
- What is the MNDPA?
- Texas Data Privacy and Security Act (TDPSA)
- Oregon Consumer Privacy Act (OCPA)
- Nebraska Data Privacy Act (NDPA)
- SWIFT CSP 2026
- CJIS v5.9.5
- Florida Digital Bill of Rights (FDBR)
- Nevada Privacy Act
- Iowa Consumer Data Protection Act (ICDPA)
- ISO 42001
- NIS2
- HITECH Act
- What is the CPRA Act?
- IRS publication 1345
- ESG
- Cyber Essentials (UK)
- ISO 27002
- UAE IA
- Personal Information Privacy Law (PIPL) of China
- Recent Frameworks
FFIEC Compliance: Requirements and How to Achieve It
June 14, 2021
GDPR (EU and UK): Principles, Rights and How to Comply
June 14, 2021
NY SHIELD Act: Requirements and How to Comply
June 14, 2021
OWASP ASVS: Application Security Verification Standard
June 14, 2021
ISO 27001: Requirements and How to Achieve Compliance
June 14, 2021
ISO/IEC 27701: PIMS Requirements and How to Comply
June 14, 2021
8 Best AI Powered GRC Tools in 2026
October 6, 2026
6 Best Operational Risk Management Software Platforms in 2026
September 3, 2026
Cyber Assessment Framework (CAF) Version 4.0
August 31, 2026
All Standards | Compliance
HITECH Act
What is the HITECH Act? The Health Information Technology for Economic and Clinical Health (HITECH) Act is a U.S. federal law that was enacted in 2009 as part of the…
What is the CPRA Act?
The California Consumer Privacy Act (CCPA) is California’s comprehensive privacy law that governs how businesses collect, use, share, and protect personal information of California residents. It originally came into force…
IRS publication 1345
What is IRS p1345? The IRS publishes guidance documents in relation to taxes. This handbook is for Authorized IRS e-file Providers of Individual Income Tax Returns, and provides rules and…
Cyber Essentials (UK)
What is Cyber Essentials (UK)? Cyber Essentials is a government-backed scheme created to help organizations of all sizes protect themselves against a wide range of common cyber attacks. It was…
Personal Information Privacy Law (PIPL) of China
What is PIPL? The Personal Information Protection Law (PIPL) is China’s comprehensive data protection law, effective from November 1st, 2021. It establishes a full privacy governance structure regulating how organizations…
DoD CMMC: Requirements and How to Achieve Certification
What is the CMMC Standard? The CMMC certification methodology was developed by the Department of Defense (DoD) to ensure that contractors have safeguards in place to secure sensitive data, such…
FFIEC Compliance: Requirements and How to Achieve It
What is the FFIEC Compliance Framework? The Federal Financial Institutions Inspection Council (FFIEC) is a structured interagency body made up of five banking regulators who are in charge of the…
HIPAA Compliance: Requirements and How to Achieve It
What is HIPAA? The Health Insurance Portability and Transparency Act of 1996 (HIPAA), is a collection of regulations that ensure the lawful use and disclosure of protected health information (PHI).…
NIST SP 800-82: ICS Security Requirements & Compliance
What is the NIST SP 800-82 framework? The National Institute of Standards and Technology (NIST) Special Publication 800-82 offers detailed assistance regarding how to protect Industrial Control Systems (ICS), that…
SOX Compliance: Requirements and How to Achieve It
What is the Sarbanes-Oxley Act? Sarbanes-Oxley Act (SOX), is a regulation that was signed into law on July 30, 2002. For compliance, all institutional investors are expected to install and…
NERC CIP Compliance: Requirements and How to Achieve It
What is NERC CIP compliance? The North American Electric Reliability Corporation (NERC) is a global regulatory authority that operates to reduce the risks associated with power grid infrastructure. This is…
NYDFS Cybersecurity Regulation: Requirements & Compliance
What is the NYDFS Cybersecurity Regulation? The New York Department of Financial Services (NYDFS) Cybersecurity Regulation (23 NYCRR 500) is a set of rules issued by the New York Department…
GDPR (EU and UK): Principles, Rights and How to Comply
What is the GDPR? The General Data Protection Regulation (GDPR) is one of the world’s most influential privacy laws, designed to protect personal data and reinforce individuals’ rights over how…
SOC 2 Type II: Requirements and How to Achieve Compliance
What is SOC 2 Type II compliance? SOC 2 (System and Organization Controls 2) is an auditing process developed by the American Institute of CPAs (AICPA). Its primary initiative is…
NIST SP 800-171: Who It Applies To & How to Comply
What is the NIST 800-171? The National Institute of Standards and Technology (NIST) is a non-regulatory agency of the U.S. Commerce Department, responsible for conducting research and establishing standards across…
NIST SP 800-53 Rev. 5: Scope, Changes & Key Enhancements
What is NIST 800-53? NIST 800-53 is a comprehensive set of guidelines developed by the National Institute of Standards and Technology (NIST) aimed at helping organizations manage and protect their…
ISA/IEC 62443: Requirements and How to Achieve Compliance
What is the ISA/IEC 62443 framework? The International Society of Automation (ISA) and the International Electrotechnical Commission (IEC) joined forces to develop the 62443 series. ISA/IEC 62443 is a non-regulatory…
PSD2: Requirements and How to Achieve Compliance
Updated November 2026: this article was written in 2021, and the PSD2 compliance deadlines below have passed. What is PSD2? The Payment Services Directive (PSD) of 2007, was replaced by…
FedRAMP Compliance: Requirements and How to Achieve It
What is FedRAMP? The Federal Risk and Authorization Management Program (FedRAMP) is a US government-wide framework that created a standardized process for assessing, authorizing and continuously monitoring cloud services security.…
ISO 27001: Requirements and How to Achieve Compliance
What is ISO/IEC 27001? ISO/IEC 27001 is a member of the ISO 27000 family of standards. The ISO 27001 standard is internationally accepted as a specification for an Information Security…
GLBA Compliance: Requirements and How to Achieve It
What is the GLBA Act? The Gramm-Leach-Bliley Act (GLBA), also recognized as the Financial Modernization Act of 1999, is a federal law in the United States that requires the protection…