

Defining Objectives within ISMS: A Strategic Blueprint
What is an ISMS? ISO/IEC 27001 defines ISMS as a systematic approach to managing information security risks…

Microsoft Puts Recall on Hold
Microsoft has announced a delay in the rollout of its controversial AI-powered Recall feature for Copilot+ PCs.…

12 Essential Risk Mitigation Strategies for 2025
Understanding the Foundation of Risk Mitigation Implementing robust risk mitigation strategies is essential to navigating the complexities…

The Pivotal Role of Self-Attestation in Ensuring Compliance
We often hear the word “self-attestation.” But what exactly does it entail, and why do some compliance…

Comprehensive Guide to NIST SP 800-171 Revision 3 Compliance
Few documents carry as much weight as the NIST Special Publication (SP) 800-171. Designed to safeguard sensitive…

Game Over? Law Enforcement Plays Hardball in Operation Endgame
In what Europol has labeled the most significant crackdown against botnets to date, Operation Endgame saw law…

Data Access Governance in Compliance and Auditing
What is Data Access Governance? 80% of digital organizations will fail because they don’t take a modern…
Best Security Questionnaire Automation Software: Top Features
In an increasingly interconnected digital landscape, the reliance on third-party vendors, partners, and service providers continues to…
How to Manage IAM Compliance and Audits
Did you know that 80% of breaches exploit legitimate identities and are difficult to detect? It’s hard…
Virtual Compliance Officers: Their Role in Modern Business
Decision-makers often grapple with the challenge of seeing cybersecurity not merely as a protective measure but as…
Boeing's Sky-High Ransomware Refusal
A grand jury indictment in New Jersey charged Russian national Dmitry Yuryevich Khoroshev with orchestrating a litany…

Manual vs Automated Risk Management: What You Need to Know
Murphy’s Law in Modern Risk Management Murphy’s Law is a timeless reminder of life’s unpredictability. Its famous…
What was Behind the Change Healthcare Breach that Shook the Healthcare Industry?
In a gripping Senate Finance Committee hearing, Change Healthcare CEO Andrew Witty disclosed that data stolen in…
External Audit: 5 Proven Strategies for Success
Have you ever navigated an external or third-party audit? What sets these audits apart is their independent…
Digital Risk Types Demystified: A Guide to Online Threats
Never underestimate the power of technology in shaping your business’s success. The digital landscape is advancing, and…
FISMA Compliance: Guide to Low, Moderate, and High Impact Levels
The Federal Information Security Modernization Act (FISMA) establishes a comprehensive strategy for enhancing the cybersecurity posture of…
Understanding the Different Types of Audit Evidence
Audit evidence lies at the heart of cybersecurity audits and assessments, providing tangible proof of an organization’s…
Zero Trust Implementation: Enhancing Security and Reducing Costs
Traditional methods no longer suffice to protect sensitive data from modern threats. Conventional strategies relied on fortress-like…
Generative AI for the Board: Navigating Legal Challenges
In today’s fast-paced business landscape, integrating Artificial Intelligence (AI), particularly Generative AI, encompassing technologies like ChatGPT, Bard,…
Microsoft Responsible for Made-in-China Hack that Targeted US Officials
A US government-backed investigation has determined that a China-sourced hack last year that infiltrated Microsoft’s networks and,…
7 Best Compliance Automation Tools: How to Choose
What is Compliance Automation? Compliance automation is like finding an underground tunnel through a (literal) mountain of…
AI Gets an Endorsement from Coalition
Coalition, a leader in cyber insurance, has added a positive endorsement for artificial intelligence (AI) to its…
Integrating Incident Response and Disaster Recovery Plans
In a world marked by the tumultuous waves of the Russia-Ukraine conflict, escalating tensions in the Middle…
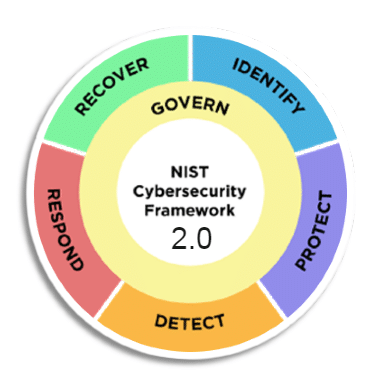
Key Updates in NIST Cybersecurity Framework 2.0
When the guys at the National Institute of Standards and Technology (NIST) released the inaugural Cybersecurity Framework…
TutaCrypt to Thwart 'Harvest Now, Decrypt Later' Attacks
Tuta Mail introduced TutaCrypt, a protocol engineered to bring email encryption into the post-quantum era. Tuta Mail…
9.8/10 Severity Flaw in Team City- Patch Now!
Hackers have recently seized upon a critical-severity authentication bypass vulnerability, CVE-2024-27198, within TeamCity On-Premises. JetBrains has swiftly…
Generative AI Governance: Balancing Innovation and Ethics
As artificial intelligence (AI) continues its march toward realization, the realm of “possible” expands with each passing…

Overview of AI Regulations and Regulatory Proposals of 2023
“AI is too important not to regulate—and too important not to regulate well,” asserts Google, capturing the…
Compliance Risk Assessment: A Strategic Guide
Compliance Risk Assessments For a Dynamic Regulatory Terrain Crafting an effective compliance program is no one-size-fits-all endeavor;…
Blackcat Claims Responsibility for the UnitedHealth Change Breach
UnitedHealth’s subsidiary, Change Healthcare, found itself at the epicenter of a cyber storm when it fell victim…